
Detection operations
Security operations
Prioritize alerts. Investigate threats. Coordinate response.
Bring the daily work of the SOC into a connected investigation process. Nova combines alert triage, risk-based prioritization, behavioral anomalies, Threat Intelligence, and proactive Threat Hunting with the affected assets and identities. Analysts can open the details behind a concern, follow related activity, and coordinate the next steps through investigation and DRX response.
Incoming signals
Priority queue
The queue should explain what deserves attention
Analysts need more than severity. Nova connects exposure, entities, confidence, behavior, intelligence and evidence quality so priority can reflect likely impact and the investigation can start with context.
From alert to investigation
- Observe
- Prioritize
- Investigate
See how work moves through Nova
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
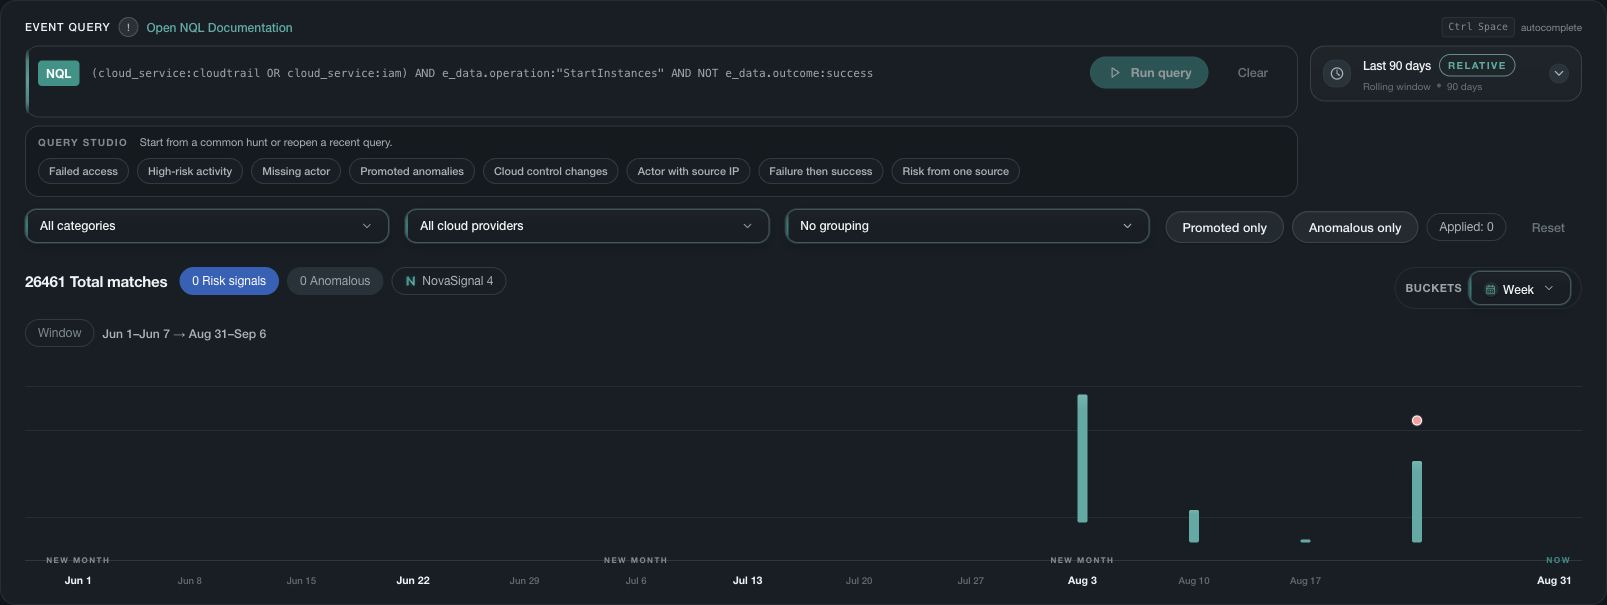
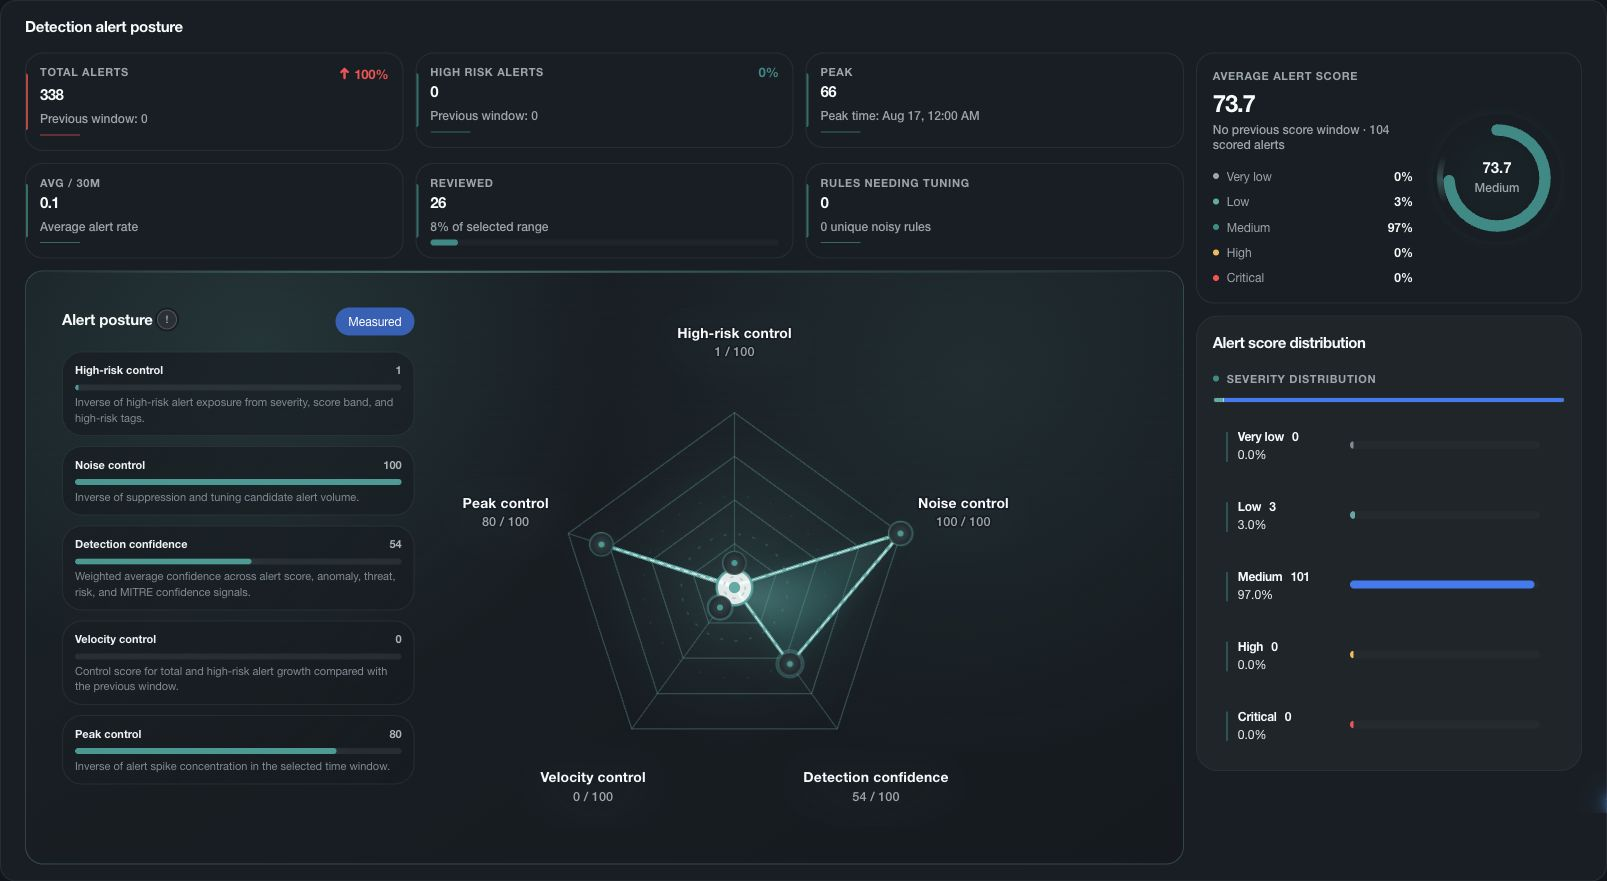
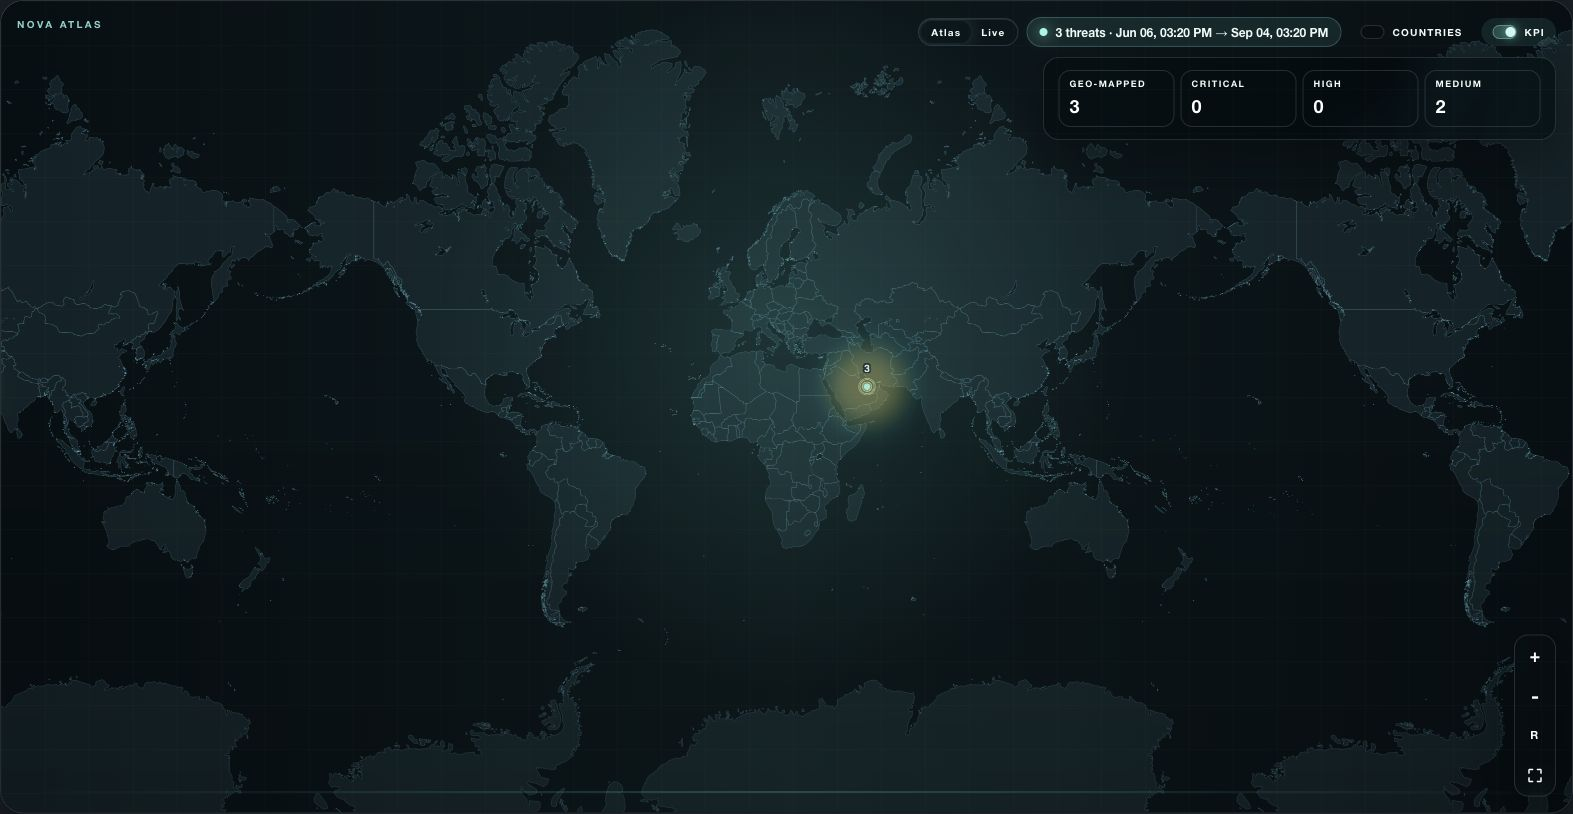
Operational workload
Make ownership, age and workflow state part of alert priority.
Teams can review unassigned work, aging items and high-risk alerts across the same queue, then move each case through a visible workflow.
Explore detection prioritization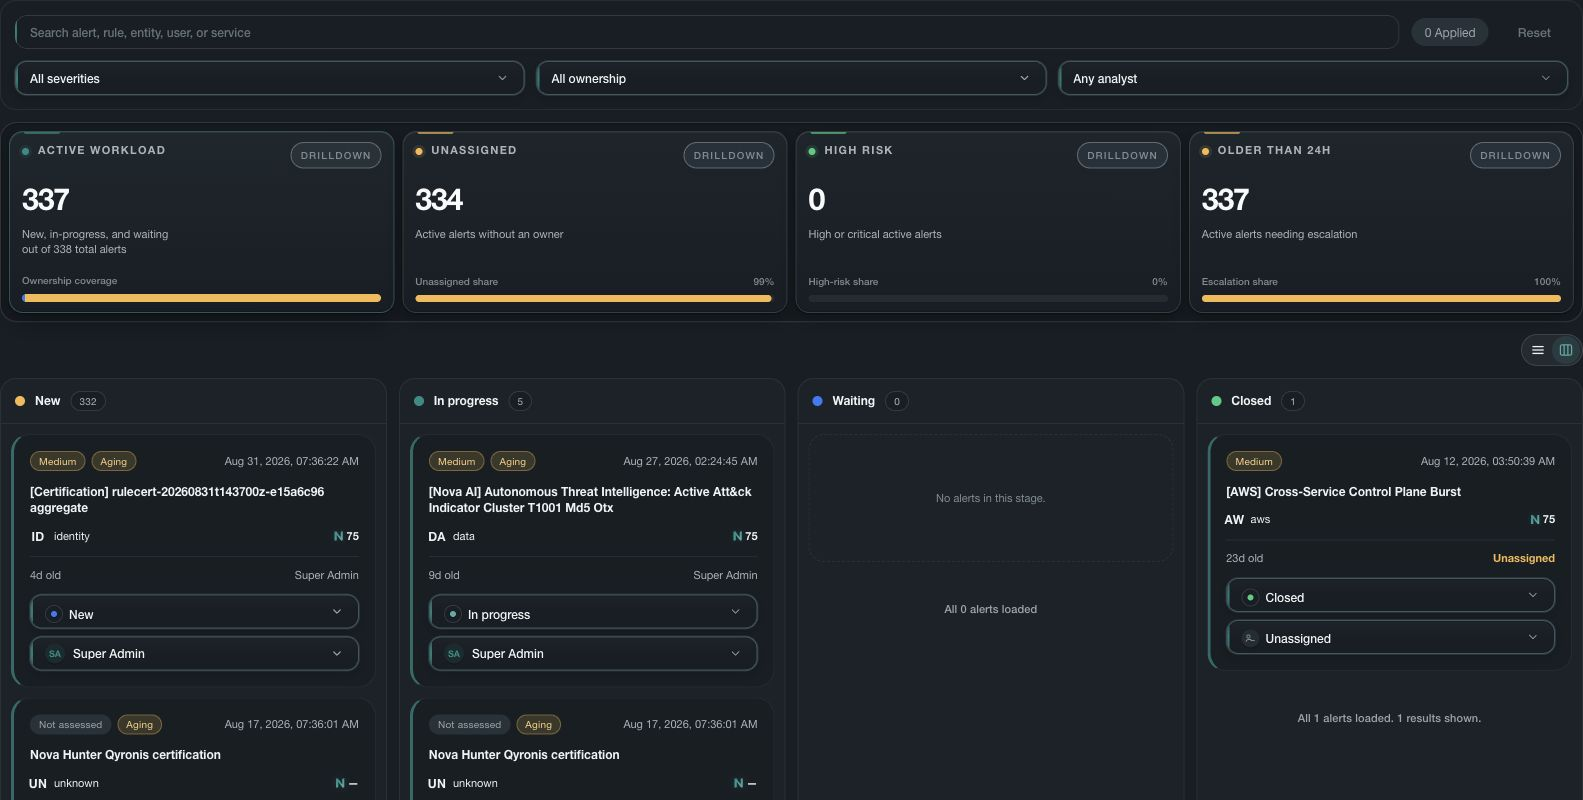
Context at first review
Start the investigation with why it triggered and what to verify next.
Priority, affected context, supporting evidence and suggested follow-up stay in the case so analysts can move from triage to validation without rebuilding it.
Explore evidence-grounded investigations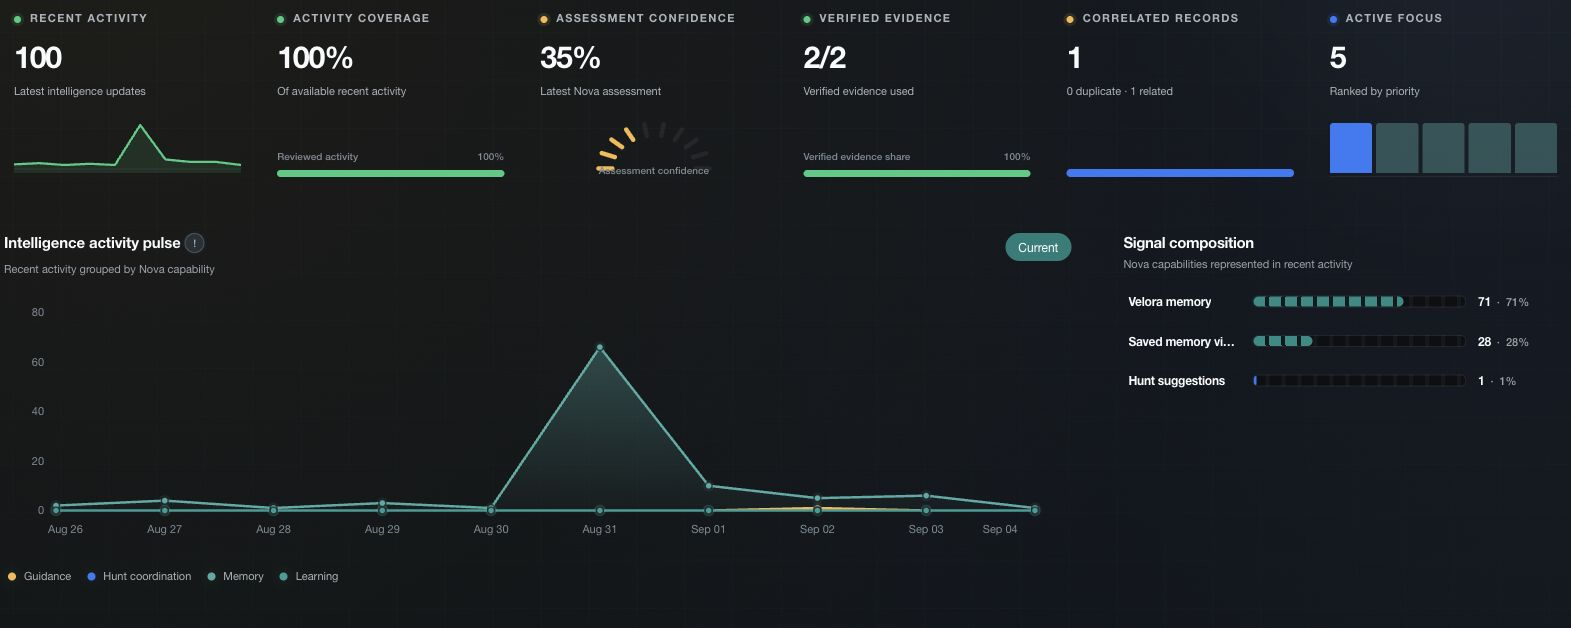
Strengthen security operations
Give analysts the context to act with confidence.
Detection and prioritization
Use NovaSignal scoring with connected evidence to explain why work deserves attention.
NOVASIGNALNovaSignal scoring engine
Review each alert's score, confidence, and contributing factors before setting its investigation priority.
ENGINEERDetection engineering
Measure coverage, review signal quality and govern proposed improvements before publication.
BEHAVIORBehavior analytics powered by Qyronis
Investigate entity change with baseline context, visible reasons, confidence and evidence state.
QYRONISQyronis behavioral intelligence
Compare unusual activity with the behavior normally seen in your organization and review the supporting events.
INTELThreat intelligence correlation
Connect supported indicators and context to observable activity and affected entities.
INVESTIGATEIncident investigation
Keep search, timeline, graph, original evidence and optional AI assistance in one case.
Nova Detection & Response eXchangeDRX incident response
For supported, connected actions, keep the decision, approval, progress and reported outcome reviewable.
PROVEReports and product health
Keep decisions and reported outcomes visible, including when a connected source is unavailable.
Evaluate Nova
See how Nova fits your cloud security workflow.
In a private briefing, we will map Nova to your stack, confirm what connects and focus the evaluation on the outcome your team cares about.