
Cloud security
Multi-cloud security
Find exposed assets. Understand attack paths. Prioritize remediation.
Understand cloud risk in the context of the resource and the activity around it. Nova brings asset inventory, CSPM findings, data exposure, access relationships, attack paths, and compliance evidence together. Teams can examine why a weakness matters, which systems may be affected, and whether related suspicious activity changes the urgency of remediation.
Understand which weaknesses need fixing first
A resource's exposure, permissions, and related suspicious activity can change the urgency of a finding. Review these details with the affected asset and the team responsible for remediation.
Cloud risk path
- Inventory
- Exposure
- Priority
See how work moves through Nova
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
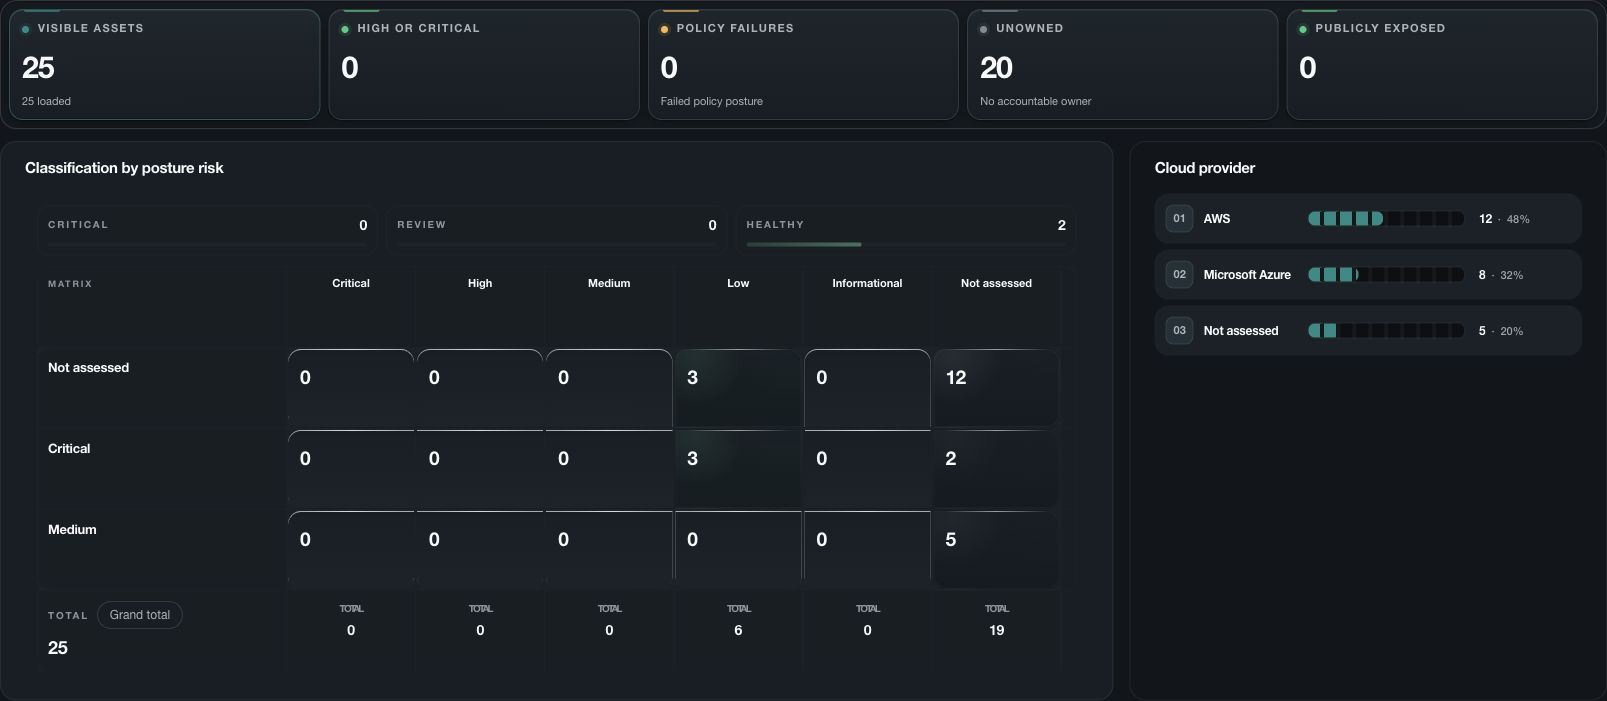
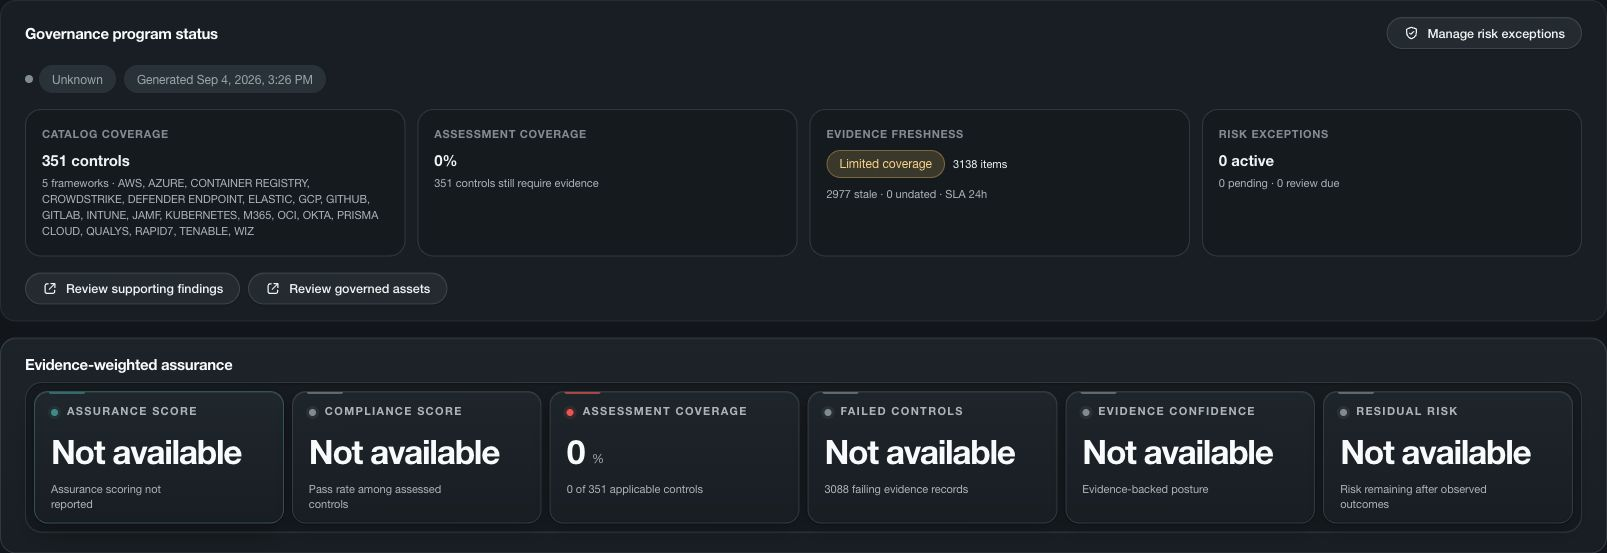
Cloud risk in context
See urgent findings, attack paths and evidence gaps in the same view.
Cloud teams can distinguish active exposure from missing assessment coverage, then focus remediation on the issues with the clearest path to impact.
Explore attack surface management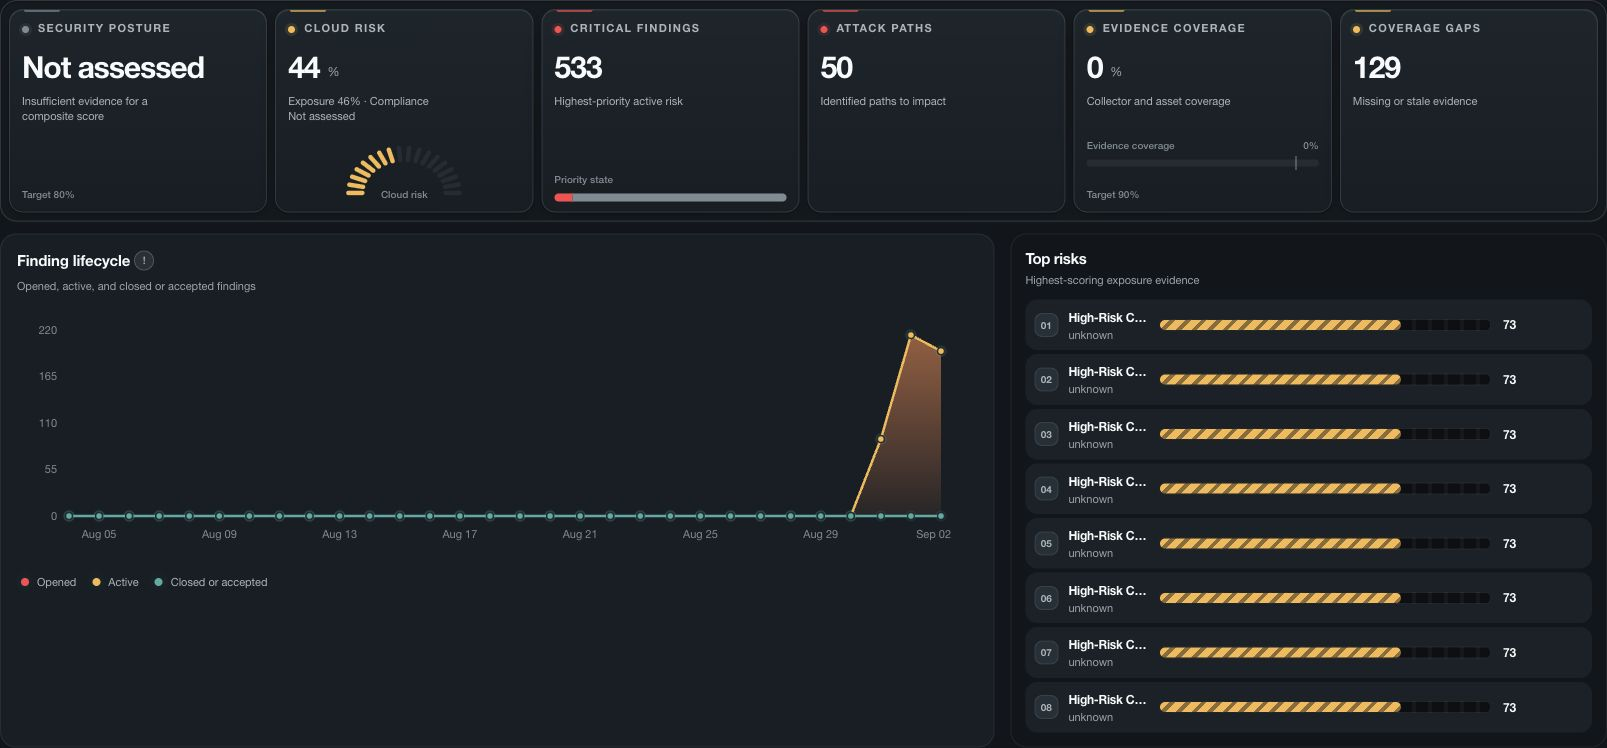
From finding to owner
Give remediation teams the affected resource and evidence they need.
Finding state, affected assets, mapped controls, ownership and risk treatment stay available in one workflow.
Review posture management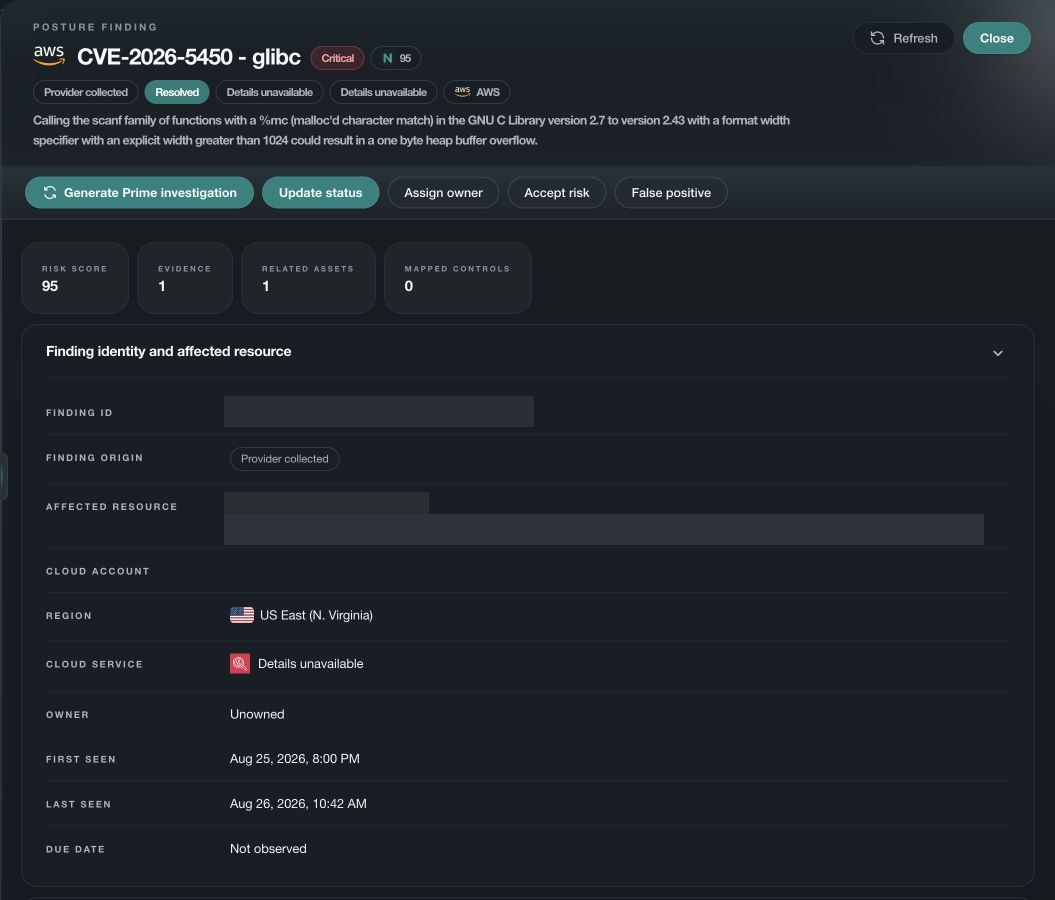
Reduce cloud risk
Prioritize the paths that can reach what matters.
Cloud security posture management
Assess supported cloud and Kubernetes configuration evidence without treating missing coverage as a pass.
CDRCloud threat detection and response
Connect cloud activity to identities, assets, exposure, threat context and supported response workflows.
ASMCloud attack surface management
Relate internet exposure, assets, identities and findings to the paths they can enable.
ATTACK PATHSAttack paths and potential impact
See entry points, relationships, reachable assets and potential impact in one investigation path.
COMPLIANCECloud compliance evidence
Distinguish assessed controls from controls with missing or incomplete evidence.
INVENTORYCloud assets and identities
Connect resource inventory and identity context to the findings and activity that affect them.
DATACloud data security
Review supported data assets with exposure, access, policy evidence and ownership context.
Nova Detection & Response eXchangeIncident response with DRX
Prepare supported actions, apply access and approval controls, and review the result.
FAQ
Questions about Cloud Security.
What is cloud security posture management?
Cloud security posture management evaluates configuration and control evidence across supported environments. Nova shows what was assessed, what failed and where evidence is missing, so an incomplete assessment does not appear as a pass.
How does Nova prioritize cloud risk?
Nova can relate findings to affected assets, exposure, identities, attack paths, active security signals and evidence quality. The available factors depend on the connected sources and are kept visible for review.
Which cloud environments and security systems can Nova connect?
Nova has evaluated connections across AWS, Microsoft Azure, Google Cloud, Kubernetes and supported identity, endpoint, software service, intelligence, ticketing and response systems. The available evidence and action set varies by connection and is confirmed for each customer environment.
Evaluate Nova
See how Nova fits your cloud security workflow.
In a private briefing, we will map Nova to your stack, confirm what connects and focus the evaluation on the outcome your team cares about.