
Trust and governance
Source health and data coverage
Know where your security visibility has gaps.
A quiet dashboard is useful only when the relevant systems are being observed. Nova helps teams review connected sources, data freshness, detection coverage, and assessments that remain incomplete. Use that picture to identify blind spots, prioritize onboarding, and explain the limits of an investigation without treating missing data as a clean result.
Expected sources
Coverage posture
No findings does not mean complete coverage
No new findings may mean no issue was found, or that the required data never arrived. Nova shows source status, the age of the data, and assessment coverage so you can tell the difference.
Response controls
- Scope
- Authorize
- Review
See how work moves through Nova
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
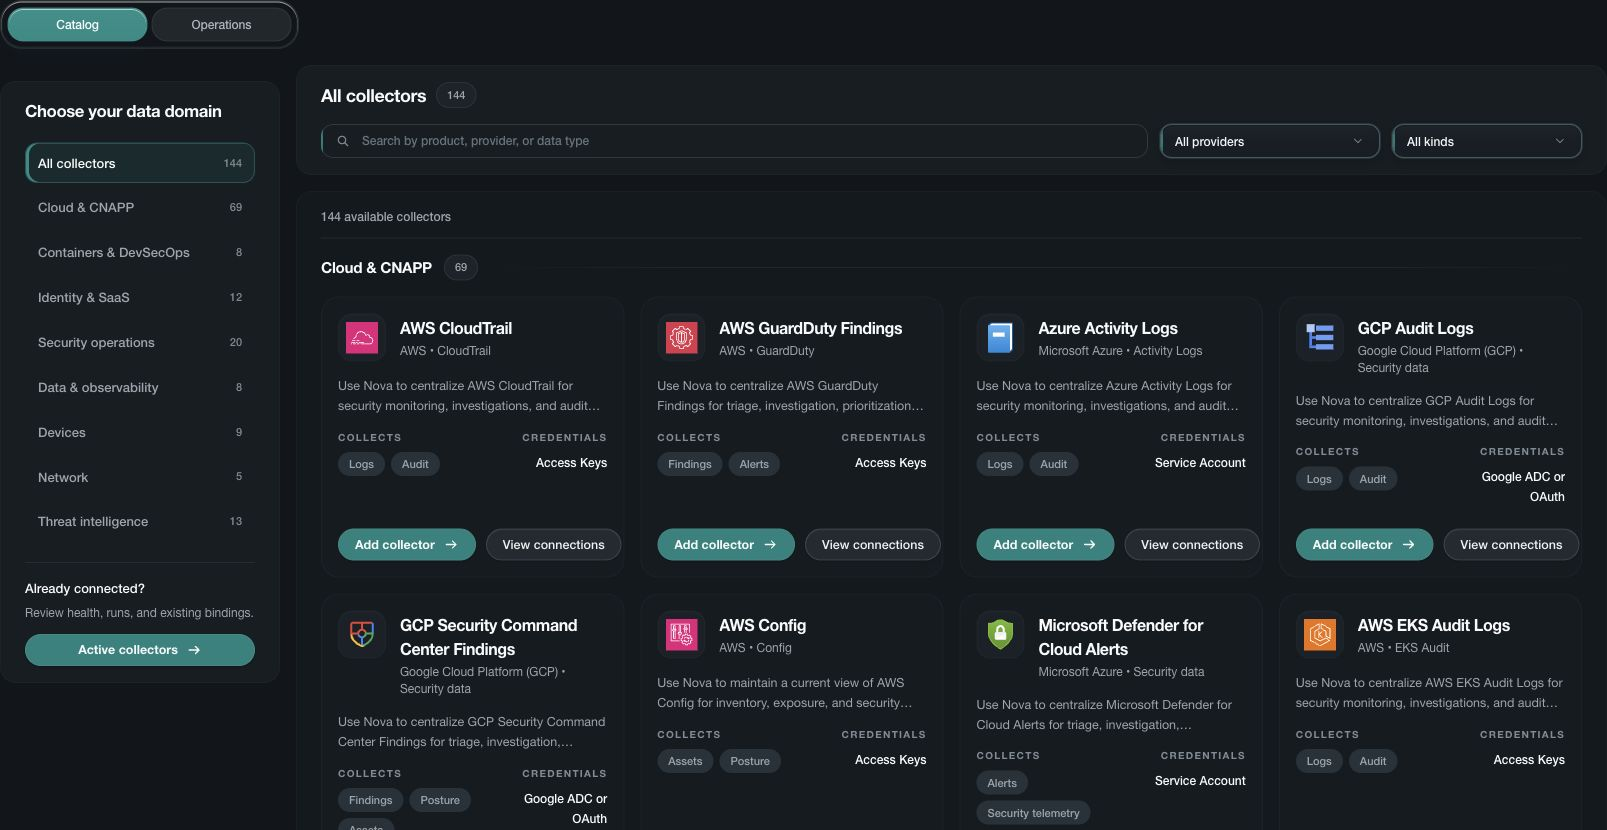
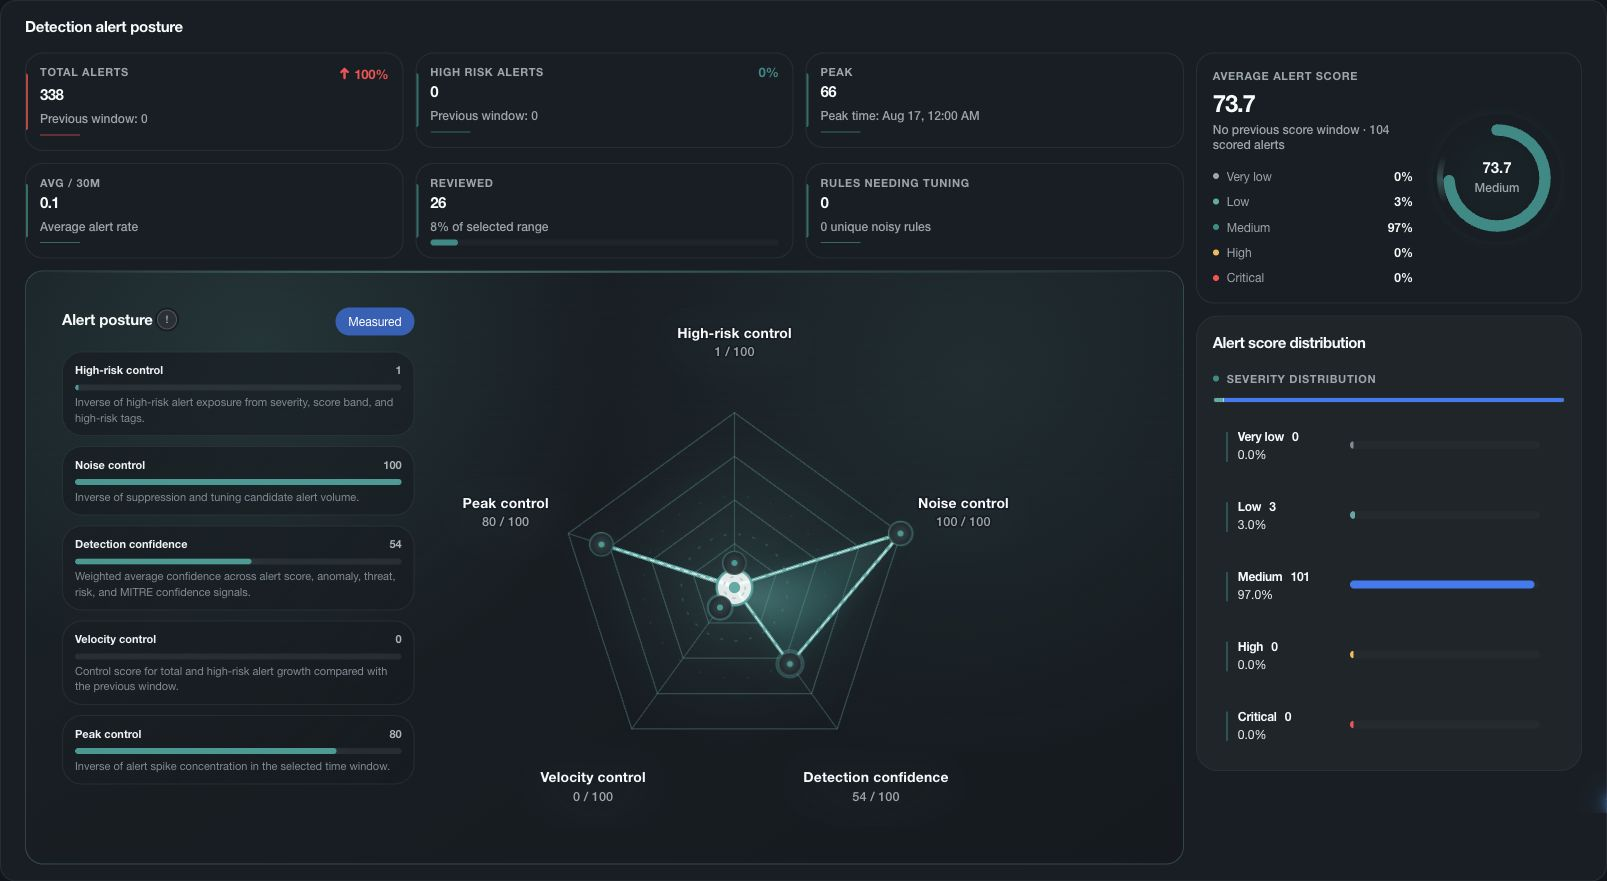
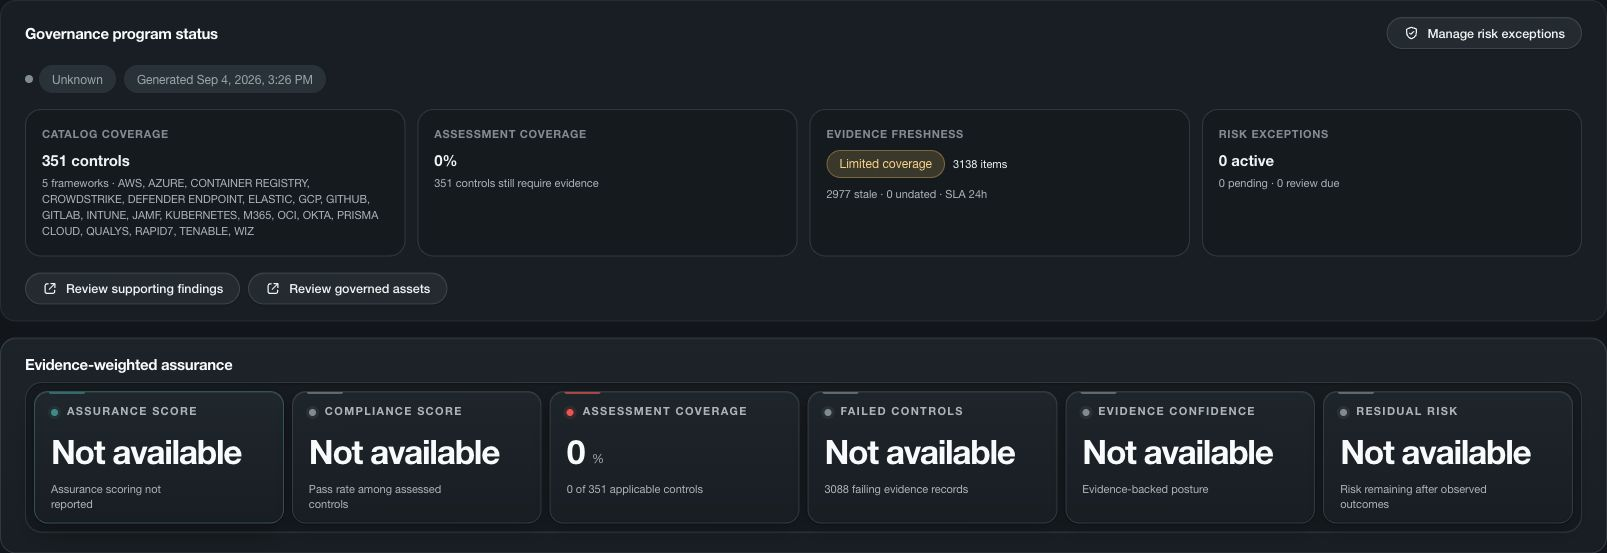
Coverage before conclusion
Show what was observed, what is stale and what remains unassessed.
Coverage state stays attached to posture and risk so a missing source cannot quietly become a passing result.
Review trust and governanceExpected sources
Coverage posture
Evidence you can follow
Move from coverage status to the activity available for investigation.
Teams can validate whether expected security activity is present, searchable and usable before relying on a detection or investigation outcome.
Explore investigationsExpected sources
Coverage posture
Coverage beside risk
Keep evidence gaps visible beside the risks they can change.
Security leaders can distinguish active risk from limited visibility and direct attention to the source, assessment or control that needs improvement.
Explore cloud risk protectionExpected sources
Coverage posture
Strengthen security operations
Give analysts the context to act with confidence.
Connected-source health
Distinguish configured, current, delayed, degraded and unavailable evidence sources.
Data freshness
Keep the age and availability of evidence visible where it changes confidence.
Assessment scope
Show which assets and controls were assessed and which remain outside available coverage.
Coverage gaps with an owner
Identify the source or assessment that needs attention and assign the follow-up.
FAQ
Questions about Security Coverage Management.
Does an empty result mean the environment is safe?
No. An empty result means no matching issue was found in the data that was assessed. It does not prove that the environment is safe. Check the selected time range, source coverage, and assessment status before drawing a conclusion.
Can coverage be reviewed across different security domains?
For supported sources, Nova relates connection and evidence state to cloud posture, detections and investigations. Exact coverage depends on the systems connected, the granted scope and the evidence available in each environment.
What access does Nova require?
Access depends on the selected evidence and response workflows. Collection should use the least privilege needed for the agreed scope. Response permissions are separate, explicit and limited to supported actions that customer policy allows.
Evaluate Nova
See how Nova fits your cloud security workflow.
In a private briefing, we will map Nova to your stack, confirm what connects and focus the evaluation on the outcome your team cares about.