
Cloud security
Cloud security posture management
Find cloud misconfigurations. Prioritize remediation.
Nova Cloud Security Posture Management assesses supported configurations across AWS, Azure, Google Cloud, and Kubernetes. Review each finding with the affected resource, severity, control evidence, and remediation guidance, then examine exposure and attack paths to decide what to address first. Missing assessment remains visible alongside the checks that were completed.
Expected sources
Coverage posture
A failed control is not the complete risk story
Teams need to know whether a weakness is reachable, which systems it affects, whether evidence is complete and what action will reduce the most credible path to impact.
Cloud risk path
- Inventory
- Exposure
- Priority
See how work moves through Nova
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
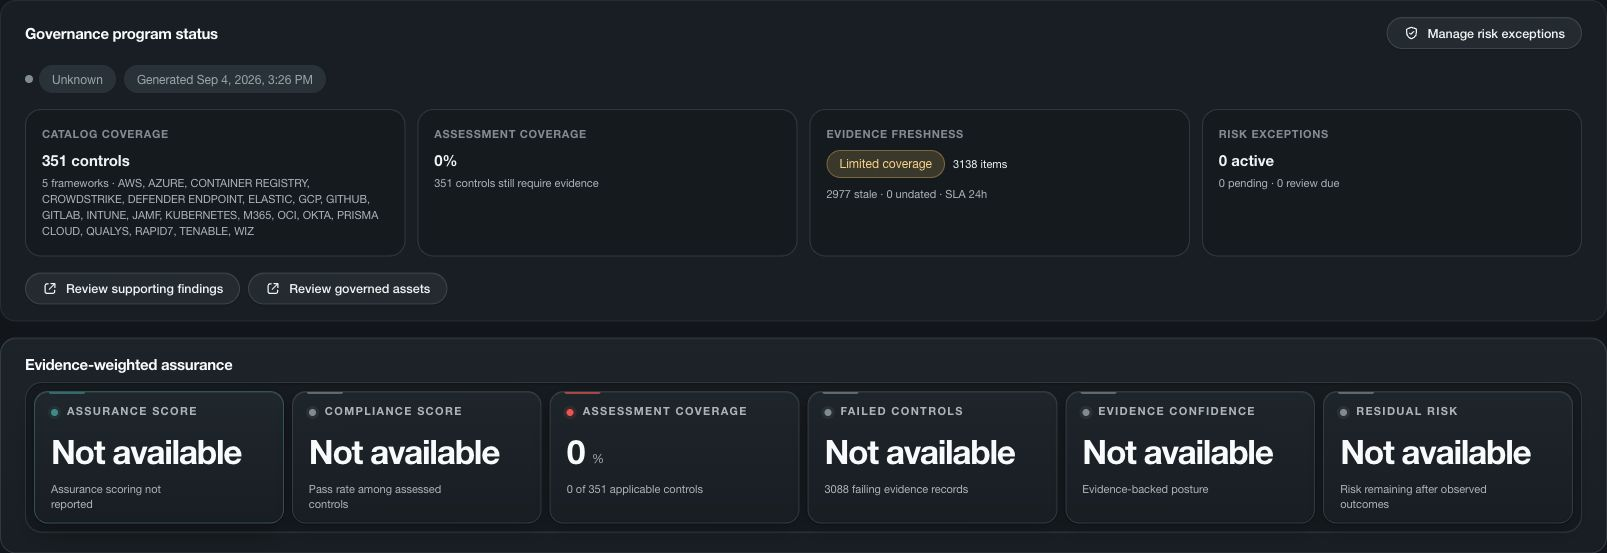
Cloud configuration findings
Prioritize exposure without treating missing coverage as safety.
Review configuration findings, attack paths, and incomplete assessments separately before choosing what to remediate.
Explore cloud security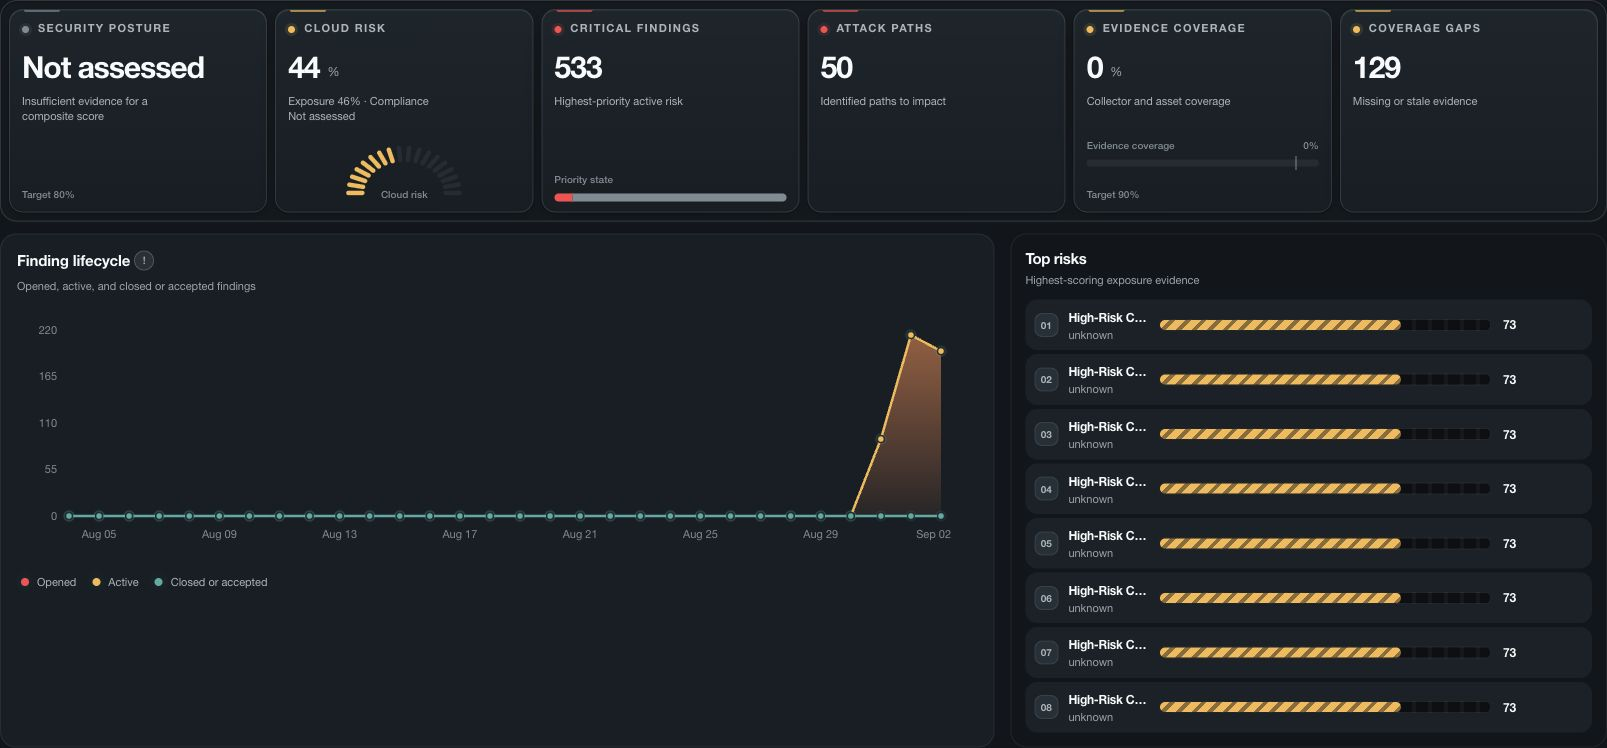
Actionable findings
Move from a control result to the affected resource and owner.
Resource identity, related assets, mapped controls, evidence and lifecycle state help teams decide what should change and who should own it.
Review cloud findings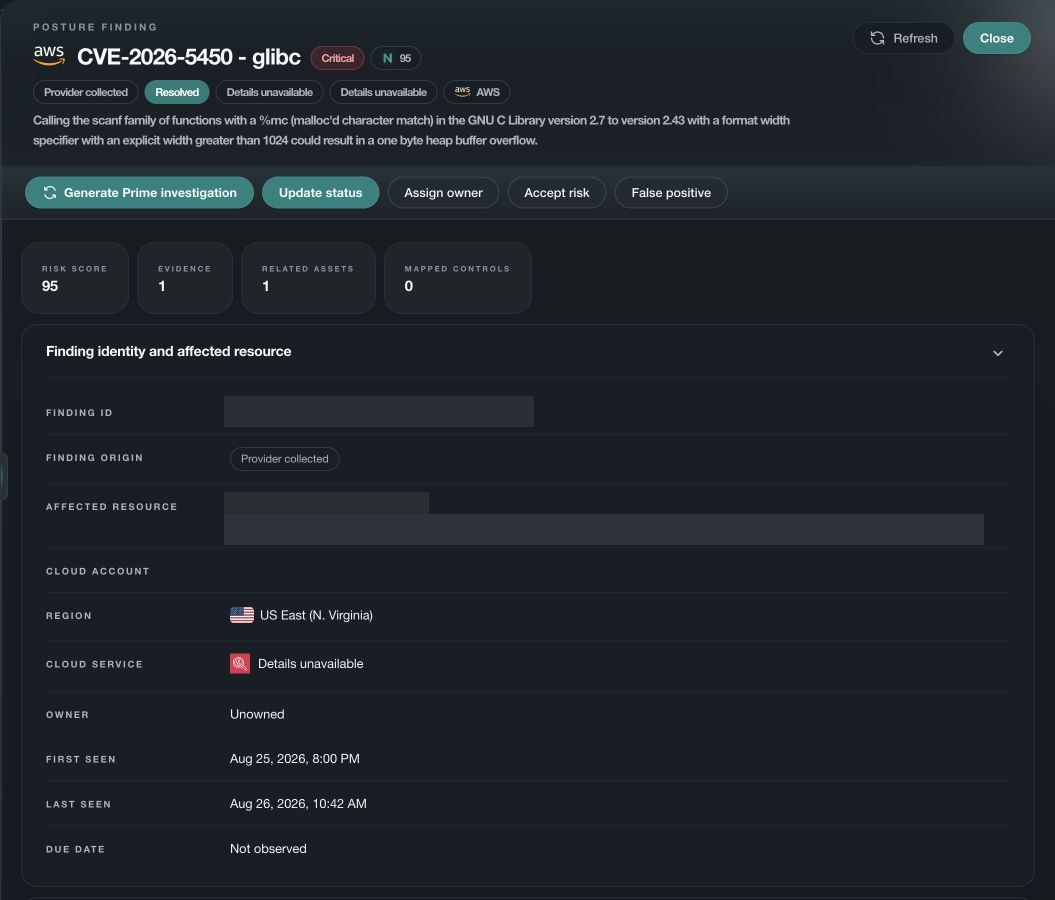
Reduce cloud risk
Prioritize the paths that can reach what matters.
Know what was checked
Show assessed, missing and incomplete evidence separately.
Exposure-aware priority
Relate control failures to reachable assets, identities and attack paths.
Compliance evidence and residual risk
Keep the evidence behind each result and the remaining risk visible.
Action-ready remediation context
Give owners the affected resource, evidence and priority needed to act.
Evaluate Nova
See how Nova fits your cloud security workflow.
In a private briefing, we will map Nova to your stack, confirm what connects and focus the evaluation on the outcome your team cares about.