
Nova ACDP
Nova ACDP. AI-Native Autonomous Cloud Defense.
Nova is an AI-Native Autonomous Cloud Defense Platform, or ACDP. It combines CNAPP capabilities for cloud asset visibility, security posture, exposure, attack paths, and compliance evidence with SecOps workflows for threat detection, behavioral analytics, threat intelligence, threat hunting, investigation, detection engineering, and governed response. Its autonomous engines connect findings to the people, resources, and activity involved while keeping evidence, uncertainty, policy, and required approvals visible.
Automated analysis, with policy and approval controls for response.
Evidence-connected defense
See how work moves through Nova
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
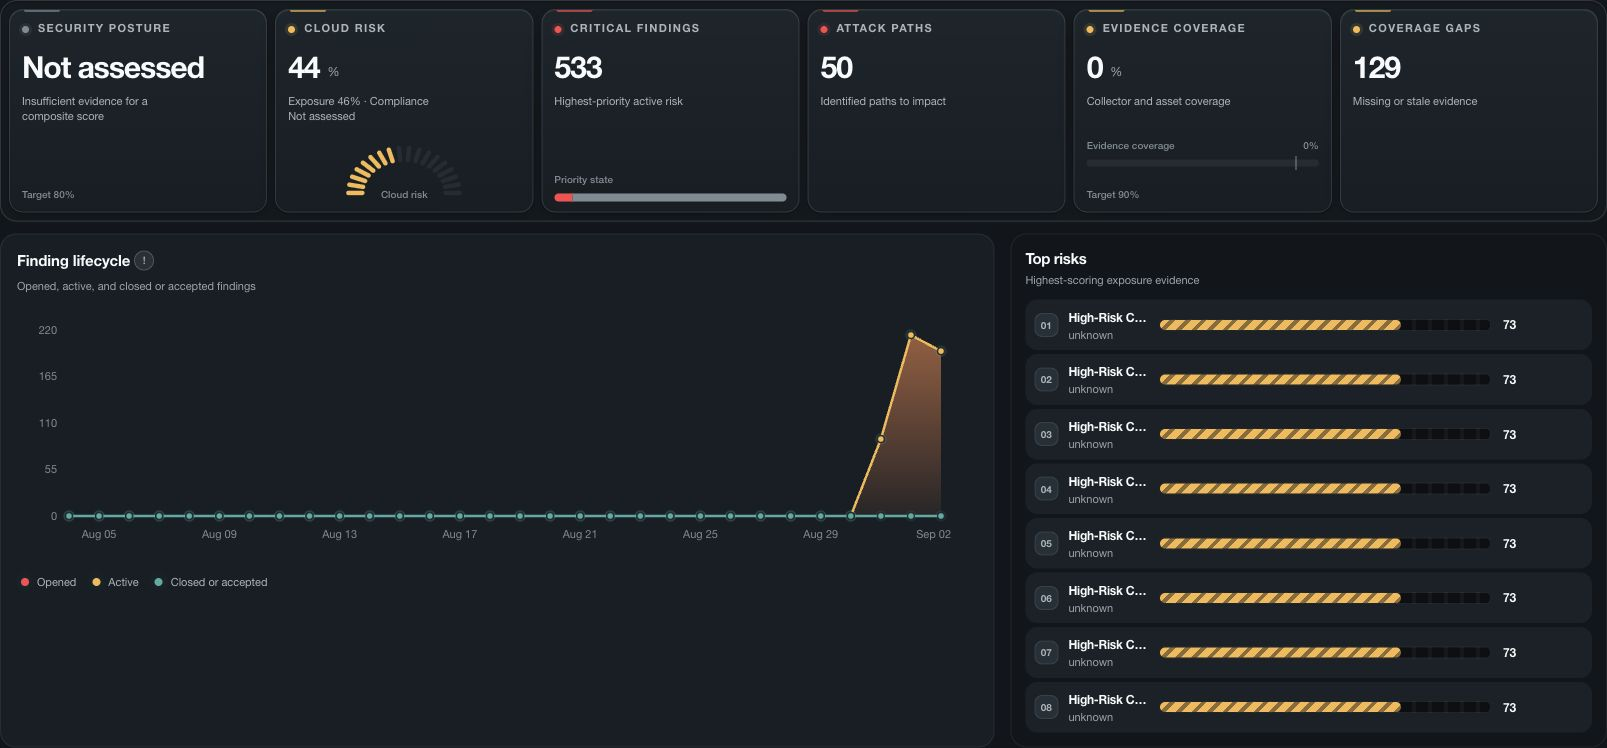
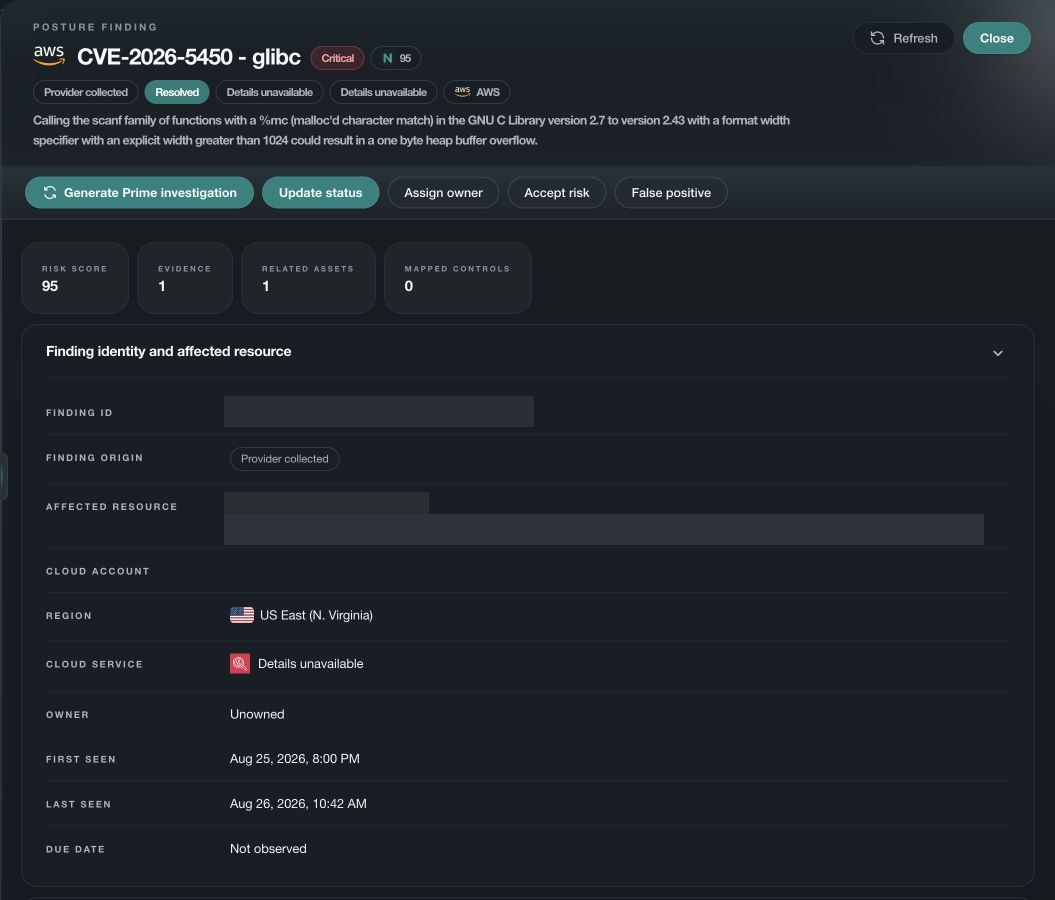
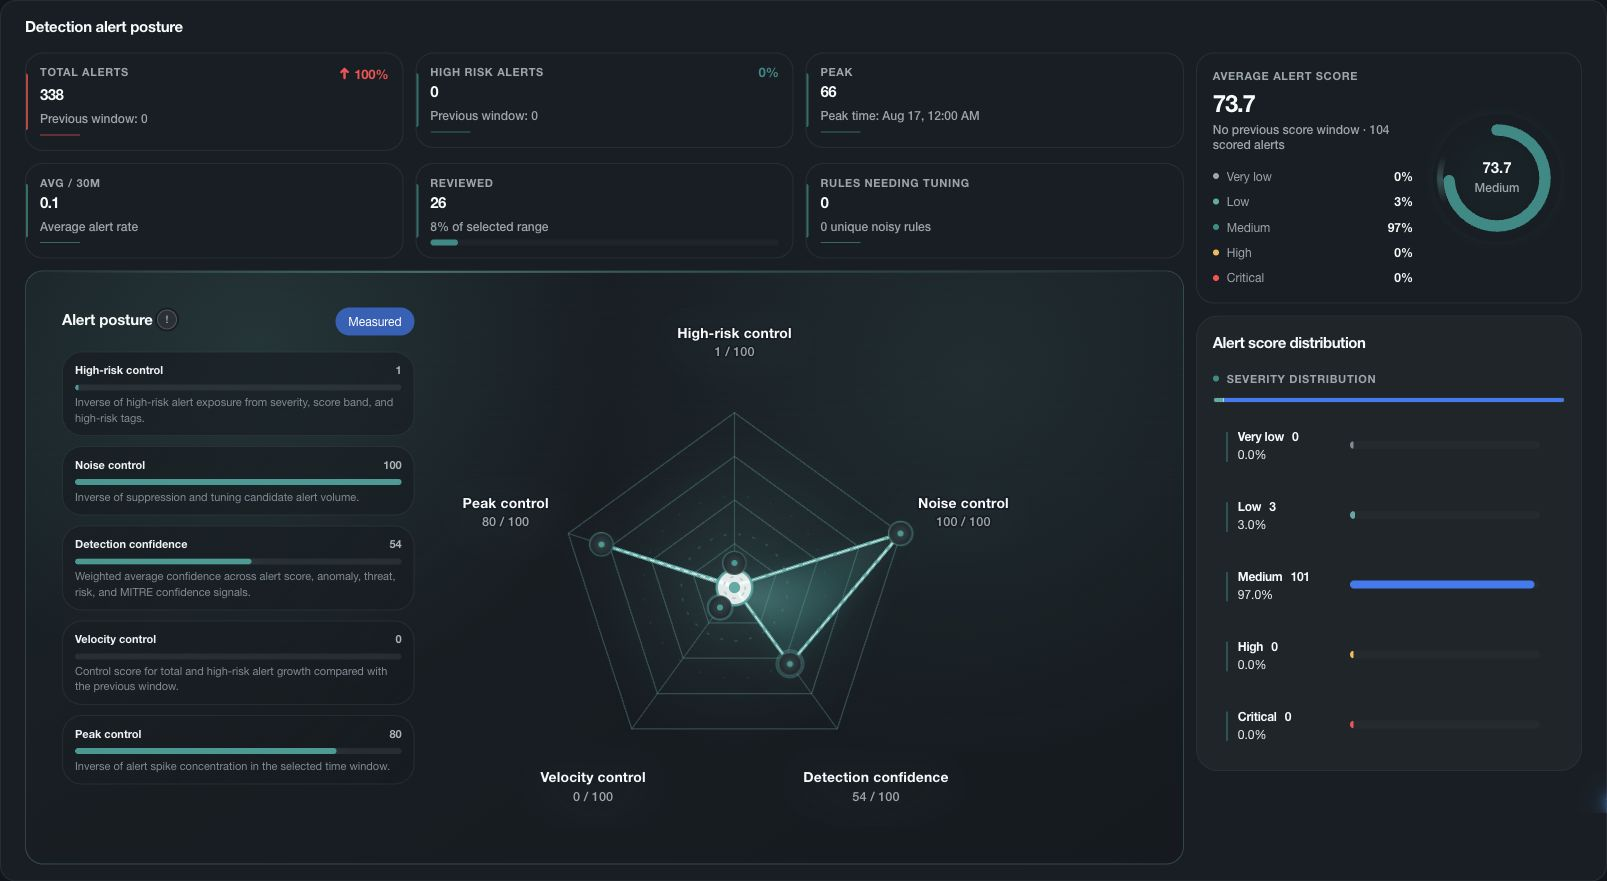
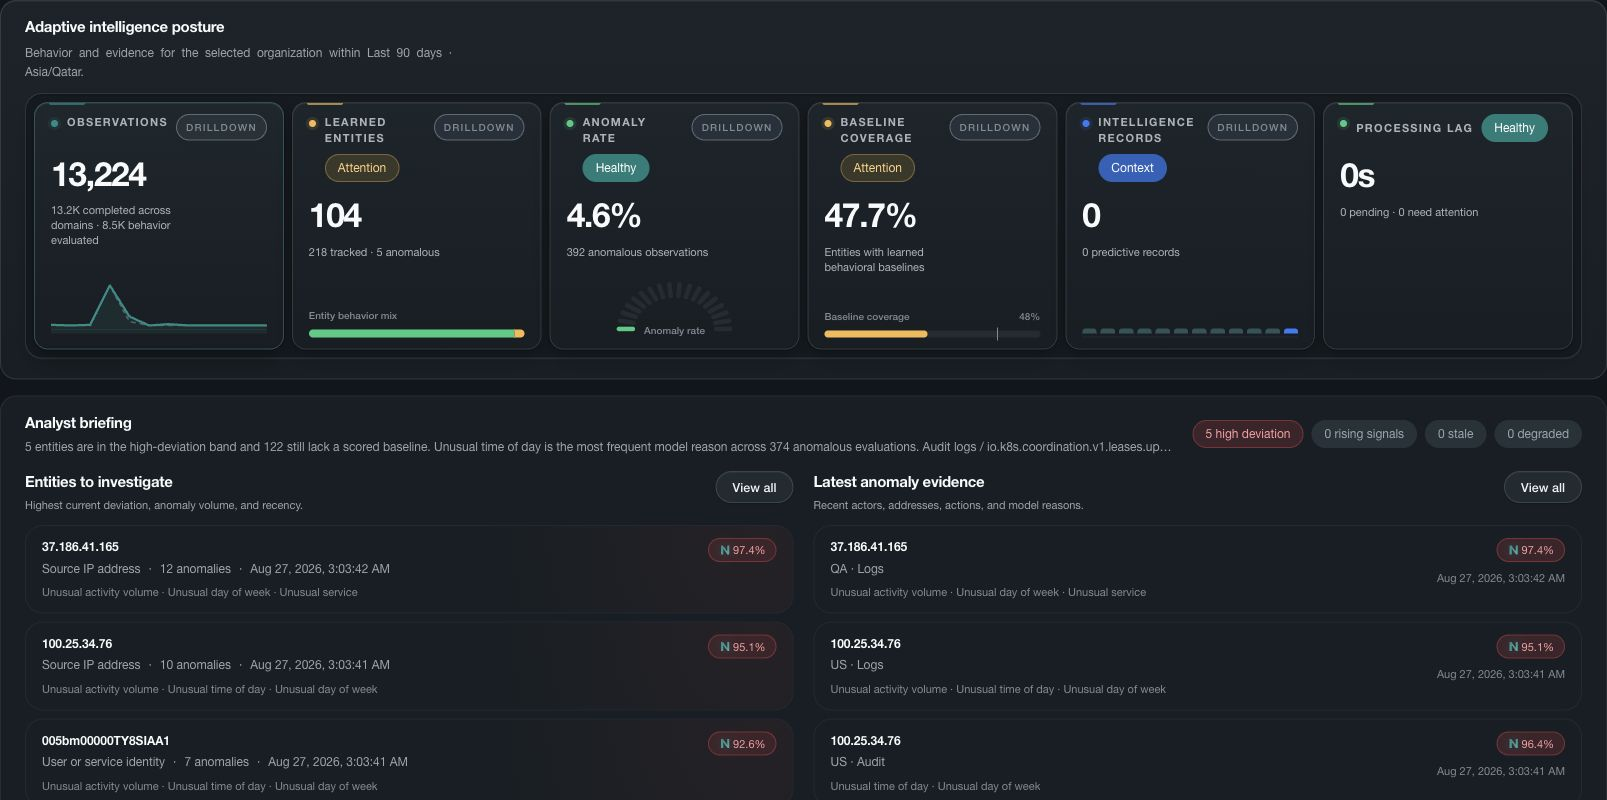
Cloud security
Know what is exposed and why it matters.
Review cloud assets, CSPM findings, data exposure, access relationships, and attack paths together. A resource's configuration is only part of its risk. Nova helps teams examine how it can be reached, which other assets may be involved, and whether related security activity changes the priority.
Use the findings and available control evidence to plan remediation and support compliance reviews. A missing assessment remains a gap to resolve, not a confirmation that a resource is secure.
Detection and security operations
Move from an alert to the activity behind it.
Nova brings alert triage, NovaSignal prioritization, behavioral anomalies, event search, and investigation into the same security workflow. Analysts can inspect an alert, follow the affected identity or resource, compare unusual activity with Qyronis baselines, and keep ownership and follow-up visible as the case develops.
Detection teams can also review rule behavior and coverage, then use NADE proposals to develop improvements. Proposed changes remain separate from active rules until the required review and validation are complete.
Threat Intelligence and Threat Hunting
Connect the wider threat picture to your environment.
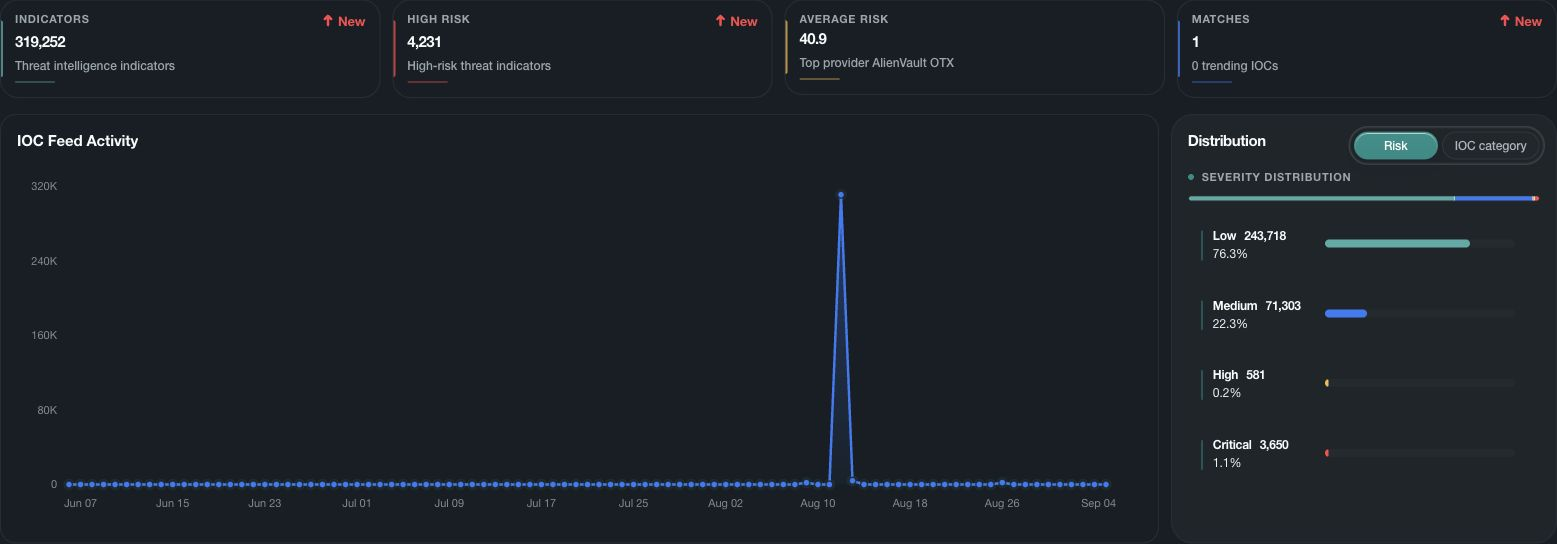
Review intelligence sources, indicator matches, and geographic activity alongside the events and assets they relate to. Threat Relevance helps focus attention on threats that matter locally, while proactive hunts examine a security question beyond existing alerts. Nova Atlas provides geographic context for detection activity and a route into the supporting detail.
Maps show where activity or indicators are associated geographically. They do not establish the identity or physical location of an attacker. Hunt conclusions remain tied to the data examined and the coverage available.
Velora security intelligence
Read the assessment. Follow the evidence.
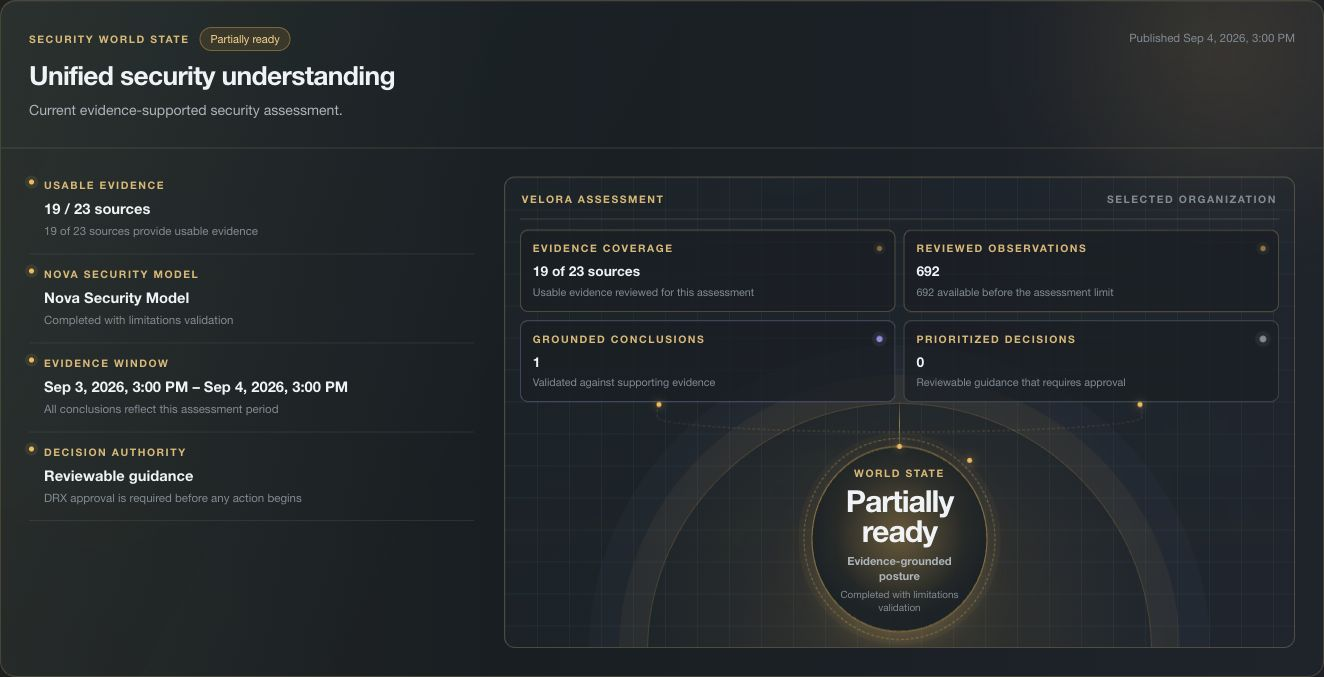
Velora connects the security picture through the command center, Autonomous Security Intelligence, Investigation Studio, and threat graph. Teams can move from current priorities to structured assessments, related entities, and source records. Reasoning distinguishes what Nova observed from supported conclusions and questions that still need investigation.
Nova Core supplies the structured investigation context. Where included, Nova Prime adds natural-language analysis and guidance with supporting references. Neither an explanation nor a recommendation grants permission to perform a response action.
Response automation
Coordinate action with the right people and tools.
DRX connects an investigation decision to supported response actions in the tools your organization uses. Teams can prepare playbooks, review the proposed change, apply approval rules, and follow execution history. The response record keeps the affected systems, responsible people, and reported outcome available for review.
The available actions depend on the provider and the approved integration. A completed request is reviewed alongside the reported result and any additional checks needed to confirm that the intended security objective was achieved.
Enterprise and MSSP operations
Keep customer boundaries clear as security work grows.
Nova supports enterprise security teams and MSSPs with customer-specific access, investigation ownership, response controls, and audit history. Supported collectors bring in the cloud, identity, endpoint, SaaS, and security evidence required for the agreed use cases. Source health and data freshness help teams understand the coverage they can rely on.
Evaluate the platform against your actual systems, responsibilities, and response requirements. Included capabilities, connection coverage, data handling, and service commitments are confirmed for your organization.
NOVA · AI-NATIVE AUTONOMOUS CLOUD DEFENSE PLATFORM
Nova connects cloud security and SOC work in one platform. Teams can assess cloud risks, investigate suspicious activity, improve detection rules, and coordinate response through supported integrations.
01 · What autonomous means in Nova
Automate the analysis. Keep control of the response.
Nova can analyze activity, prioritize alerts, and prepare detection improvements automatically when the required data and controls are available. Teams can review the results and supporting information. Response actions still follow the configured permissions, policies, and approvals.
Review cloud risks and active threats
Review misconfigurations, suspicious activity, threat intelligence, and data coverage together to understand what needs attention.
Look for emerging risks
Use past activity, unusual changes, and possible attack scenarios to identify issues that need investigation.
Review the explanation
Check the supporting events, confidence, and missing information behind each recommendation.
Control response actions
Supported actions must follow your organization's access rules, policies, and approval requirements. High-impact actions remain under the required human approval controls.
02 · Nova engines
Specialized intelligence across the security lifecycle.
Qyronis explains behavioral change. NovaSignal helps prioritize alerts. NADE proposes detection improvements. Velora connects evidence and reasons through security questions. RAZE models attack scenarios, and DRX manages supported response actions. VFP adds recurring-pattern intelligence through controlled evaluations. These capabilities have distinct roles and availability, with the underlying evidence available for review.
Qyronis
Detect unusual activity by comparing it with the behavior normally seen in your organization.
02 · PrioritizeNovaSignal
Prioritize alerts using risk scores, related activity, and an explanation of the factors behind each score.
03 · ImproveNova Autonomous Detection Engine
Identify detection gaps and propose rule improvements for your team to test and approve.
04 · ReasonVelora
Help analysts understand an investigation, review supporting evidence, and decide what to check next.
05 · Emerging PatternsVelora Federated Patterns
Identify recurring threat patterns and propose threat hunts and detection improvements for review.
06 · ModelRed-team Adversary eXecution Engine
Explore possible attack scenarios and detection gaps through analysis, without carrying out destructive attacks.
07 · GovernNova Detection & Response eXchange
Coordinate supported response actions with policy checks, approvals, and a record of the result.
03 · Response controls
Know what was recommended, approved, and completed.
A suggested action, an approved action, and a completed action are different stages. Nova keeps their status and reported results available so your team can review what happened.
- Analysis depends on the data Nova has available to assess.
- A recommendation or simulation does not grant permission to run an action.
- High-impact action remains subject to configured human approval and separation of duties.
- Missing or degraded evidence is shown as such. It is never converted into assurance.
FAQ
Questions about Nova ACDP.
What makes Nova one connected platform?
The same authorized evidence can inform cloud risk, detection, investigation, supported response and reporting. Nova keeps source, confidence, coverage and decision context attached instead of flattening every signal into one unexplained score.
Which security domains does Nova bring together?
Nova covers cloud asset inventory, configuration checks, data exposure, attack surface management, and compliance evidence. SOC teams can use alert triage, behavior analytics, threat intelligence, threat hunting, detection engineering, investigation, and supported response actions.
Is Nova a CNAPP?
Nova includes CNAPP capabilities for cloud asset inventory, Cloud Security Posture Management, external exposure, attack paths, cloud data context, supported code and workload checks, compliance evidence, and cloud threat detection. Nova is positioned as an ACDP because it carries that cloud context into SecOps prioritization, investigation, autonomous analysis, detection improvement, and governed response.
How do Nova’s seven engines work together?
Explore Nova's engines for behavior analytics, alert prioritization, detection engineering, AI-assisted investigation, threat patterns, attack modeling, and response.
Can Nova work with an existing security stack?
Yes, where the required connection is supported. Nova can connect cloud, identity, endpoint, software service, intelligence, ticketing and response systems. Hansec confirms the exact evidence, action and permission coverage for each environment.
Is Nova a SIEM replacement?
Nova includes event search, detection, investigation and response workflows, and it can work with existing security systems. Whether it replaces any current tool depends on the required data sources, retention, workflows and controls in the customer environment.
Which teams is Nova designed for?
Nova is designed for enterprise security operations, cloud security, detection engineering, security leadership and managed security service teams that need evidence-backed decisions, separated customer boundaries and controlled response.
Evaluate Nova ACDP
See how Nova ACDP fits your environment.
Review your cloud accounts, security tools, and response requirements with Hansec. We will identify the supported connections and relevant Nova capabilities for your evaluation.