
Nova platform
Cloud security and SOC collaboration
Cloud risk and active threats belong in the same investigation.
An exposed resource, a suspicious identity, and an alert may describe different parts of the same security problem. Nova connects cloud posture, behavioral change, threat intelligence, and investigation evidence so teams can assess them together. Analysts keep access to the source details and can move from that assessment to reviewed detection improvements or supported response.
Observed sequence
Assessment
Keep investigation details together
Review original events, related assets, analyst findings, and response history in the same investigation. Your team can understand how the case developed and why an action was taken.
Security workflow
- Connect
- Contextualize
- Decide
See how work moves through Nova
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
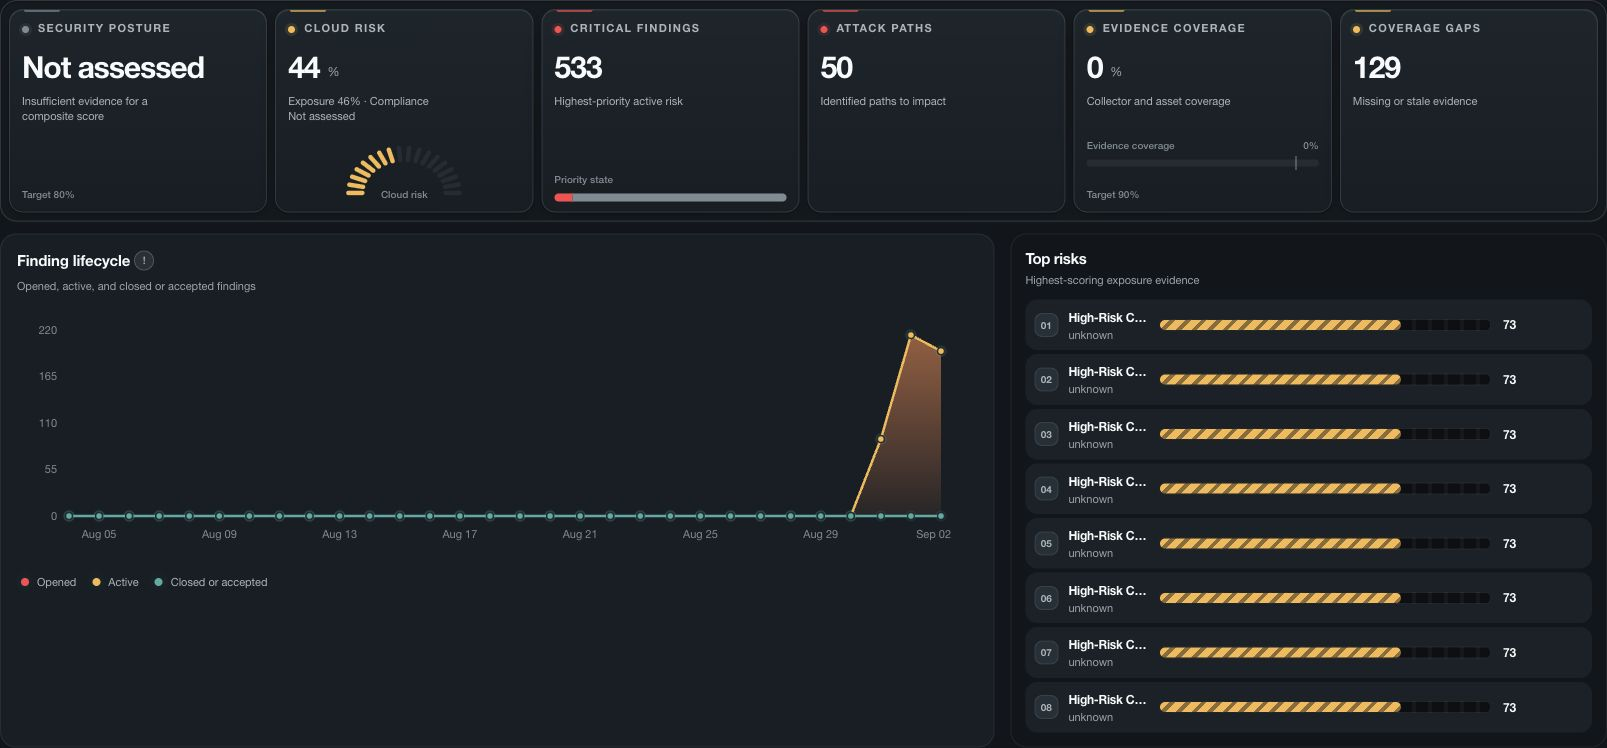
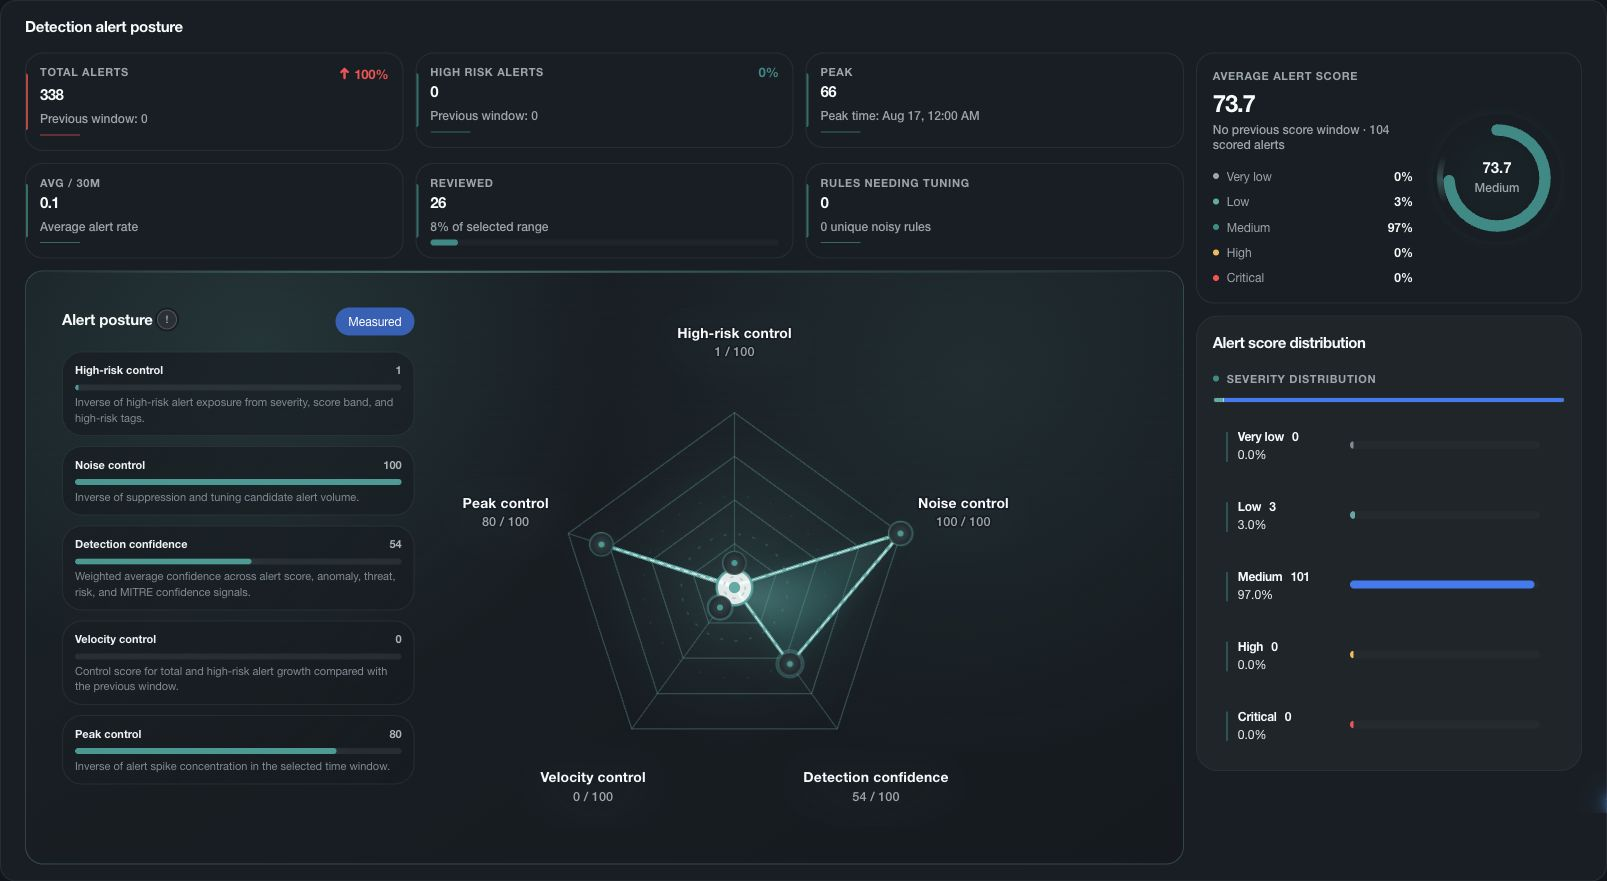
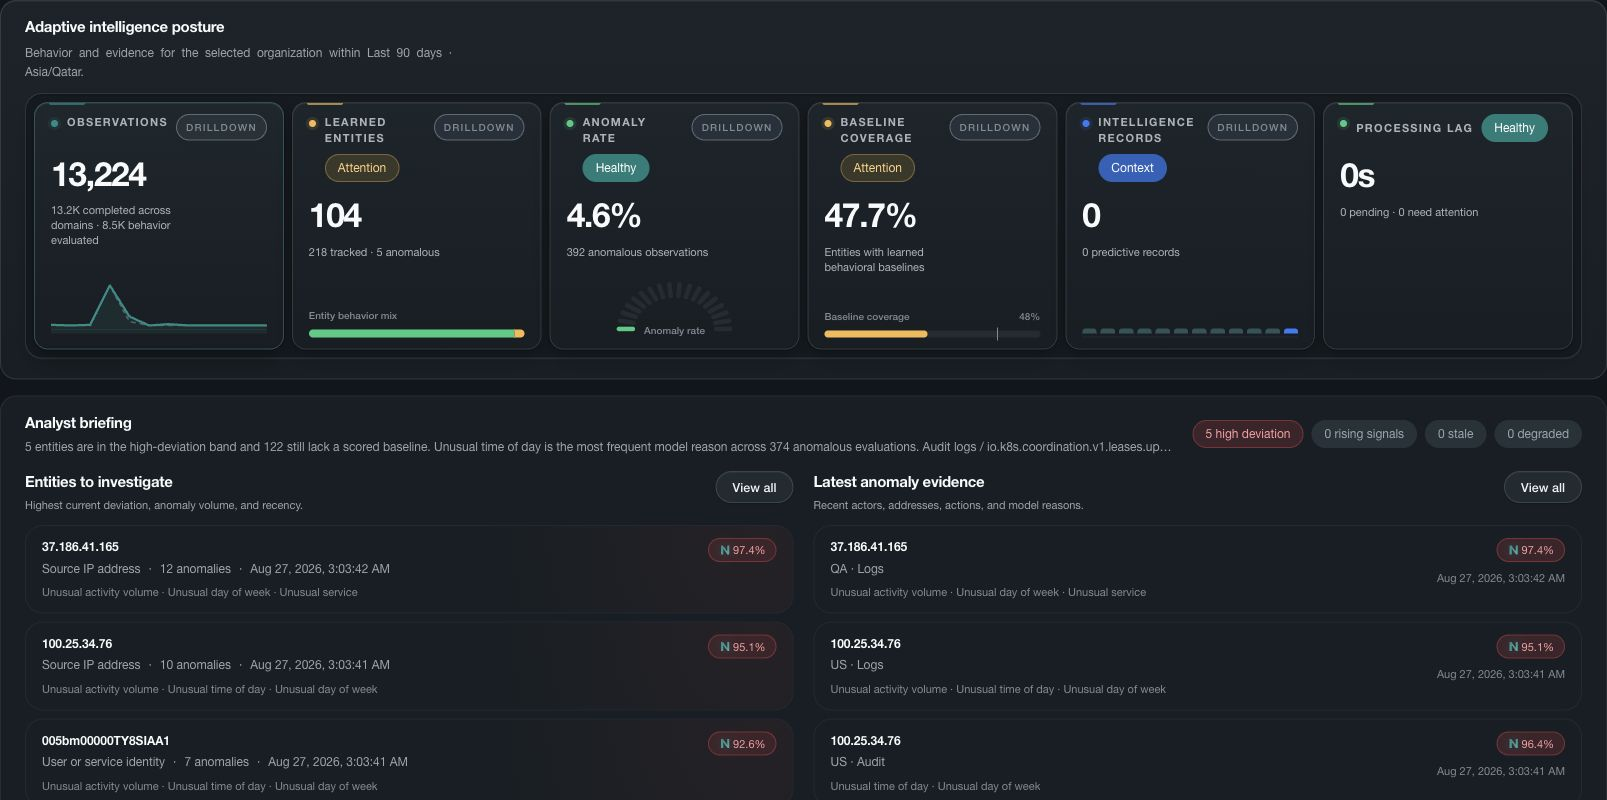
Clear assessment status
Know when the evidence supports a decision, and when it does not.
Coverage, confidence, conflicts and unknowns remain visible beside the assessment, so incomplete evidence cannot become a confident conclusion.
Explore the investigation approach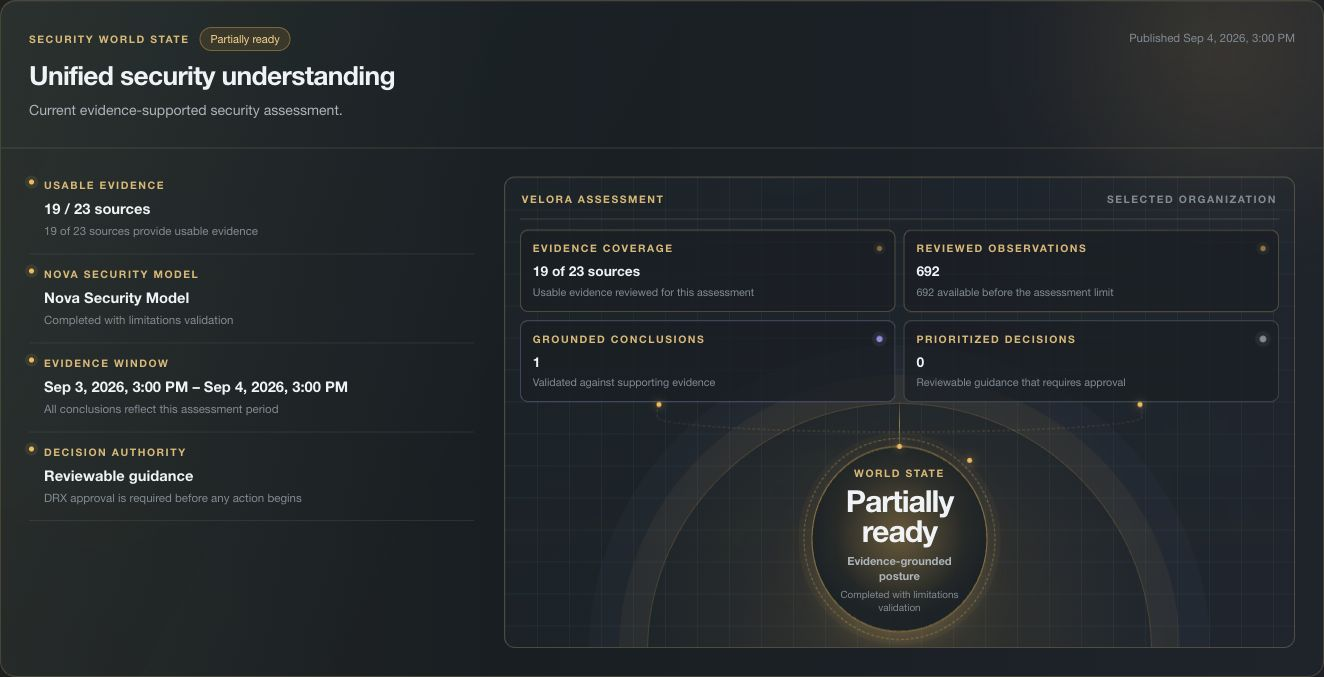
Analyst review
Improve detections with review built into the workflow.
Proposed changes can move through validation and analyst approval before joining the rule library, keeping control with the team that owns the outcome.
Explore Velora intelligence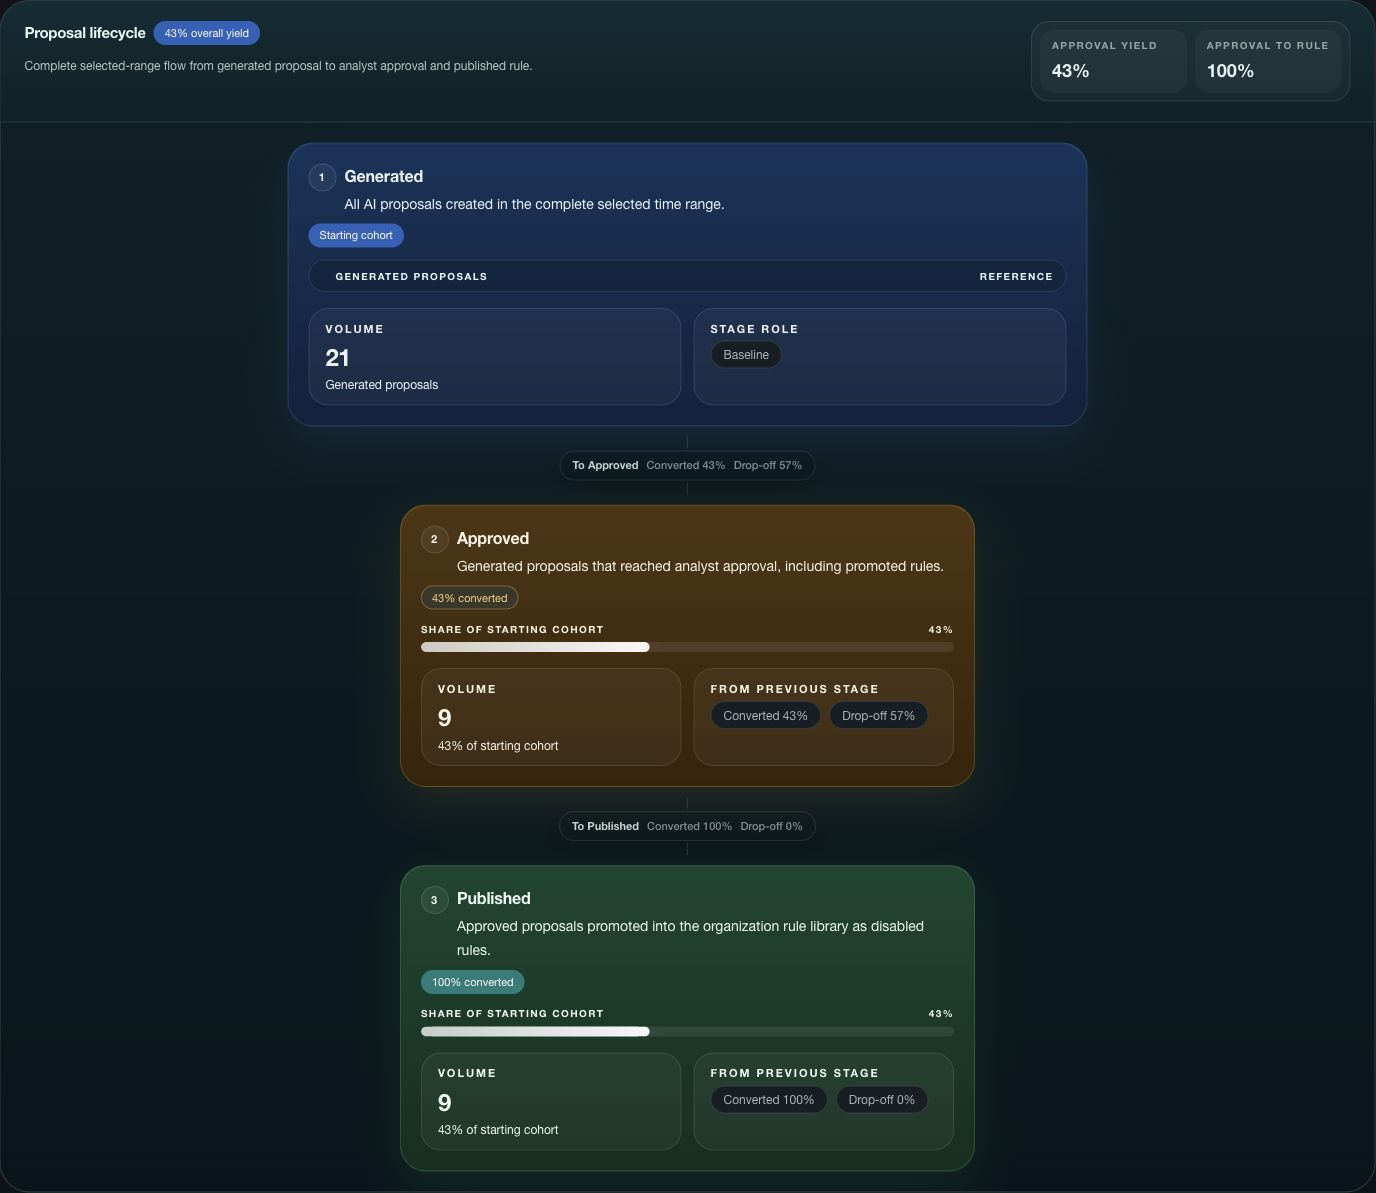
From alert to response
Follow an incident from the first alert to the response.
Know what was observed
What arrived, what is current and what is missing stays visible.
Know why it matters
Risk is explained through evidence, relationships and affected systems.
Know who authorized action
For supported actions, response keeps the decision, approval, progress and reported outcome attached.
Cloud security and SOC collaboration
Review the evidence before choosing the next step.
AI assistance, not AI dependence
Core investigation remains available without generative AI. Optional assistance adds explanations tied to evidence analysts can verify.
Alert context in one place
Alerts can be evaluated beside affected assets, exposure, posture, identities and intelligence rather than in isolation.
Automation keeps human control
Permissions, simulation and required approvals control supported actions, while reported outcomes remain reviewable.
Built for enterprise and MSSP teams
Reusable workflows preserve each customer’s data, ownership and permissions.
Know what the findings are based on.
Missing data does not mean there is no risk.
Nova shows the sources used, the confidence in its findings and gaps in coverage. Analysts can see when more information is needed before drawing a conclusion.
Evidence before conclusion
The original sources and confidence stay available for analyst review.
Control before high-impact action
The responsible owner and required checkpoint stay visible before action.
Blind spots stay visible
Missing or incomplete evidence never appears as an all-clear.
Evaluate Nova
See how Nova fits your cloud security workflow.
In a private briefing, we will map Nova to your stack, confirm what connects and focus the evaluation on the outcome your team cares about.