
Cloud security
Cloud resource inventory
Know what you have, and what changes its risk.
Build a security view of the cloud resources Nova can observe, organized by provider, account, region, and service. Open an asset to review its configuration, ownership, related findings, and exposure. The inventory provides a starting point for understanding how a resource is used and where it fits into a wider investigation.
Expected sources
Coverage posture
Move from a resource list to the details you need
Teams need more than a resource name. They need provider and service identity, location, exposure state, posture evidence, ownership and the activity that may change priority.
Cloud risk path
- Inventory
- Exposure
- Priority
See how work moves through Nova
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
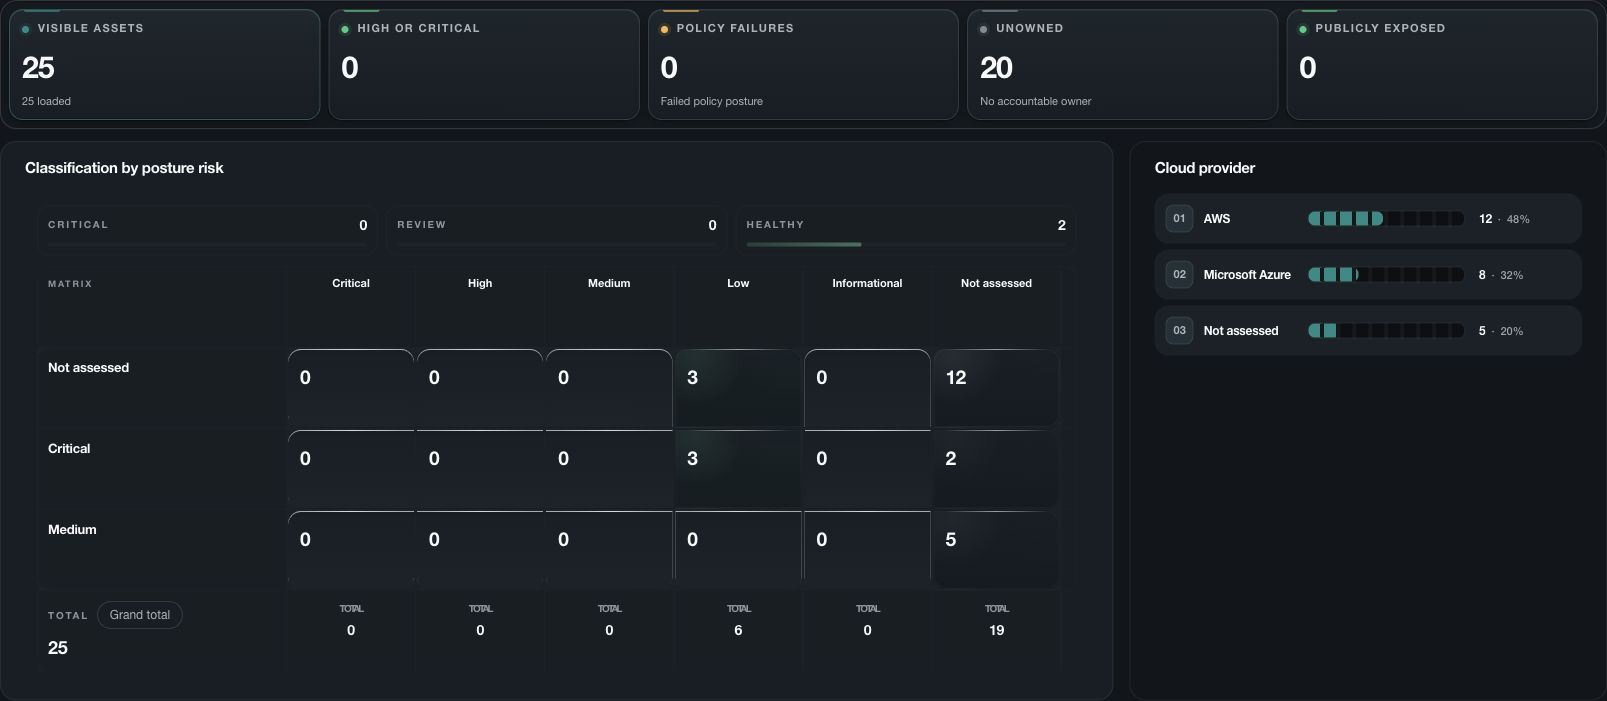
Inventory connected to risk
Move from the estate view to the cloud risks that need attention.
Review findings, attack paths, and missing assessments alongside the asset inventory.
Explore cloud security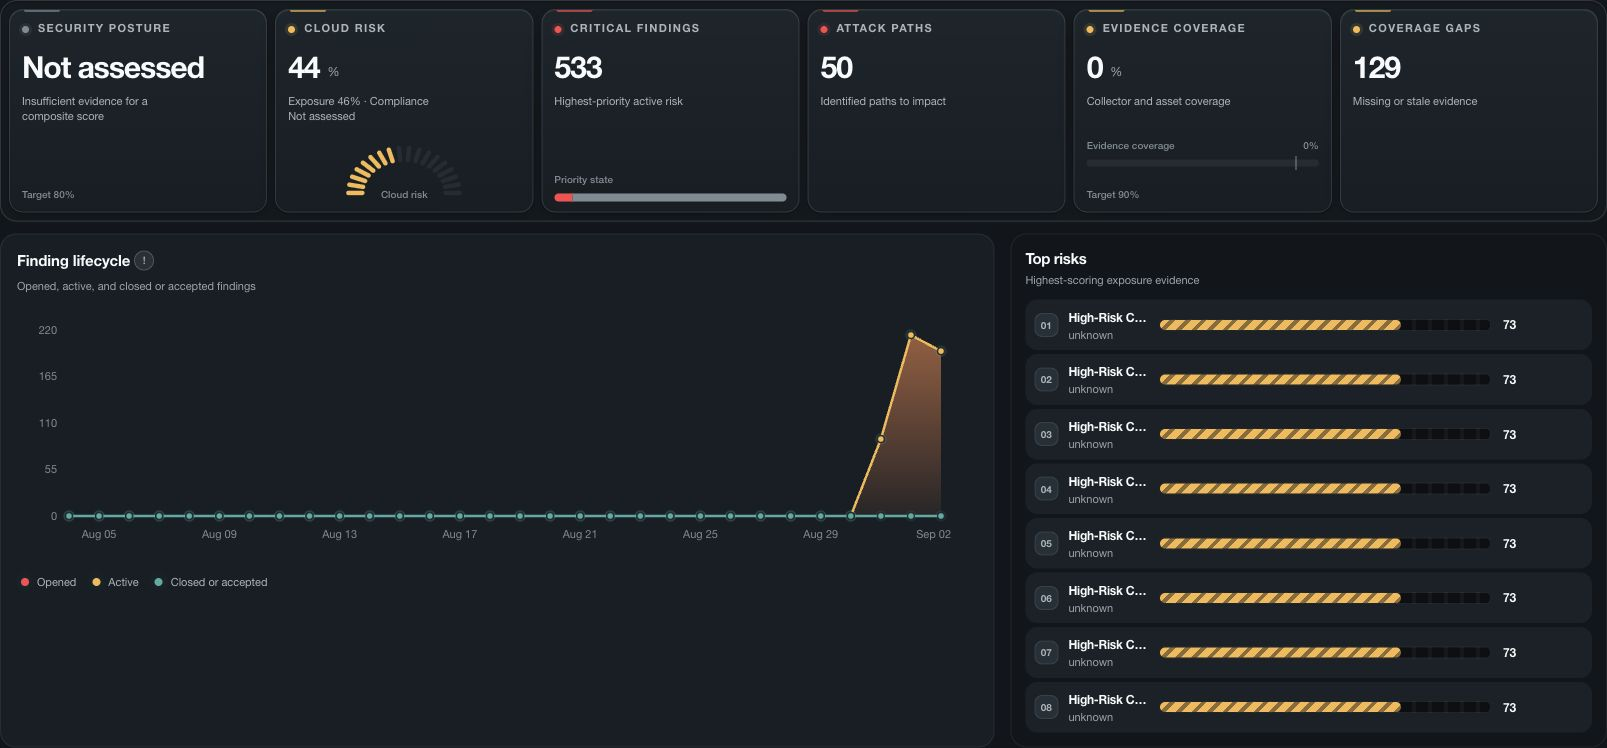
Resource-level context
Open an asset with its identity, exposure and management history intact.
Provider, account, region, service, owner and available policy evidence stay connected to the resource under review.
Review attack-surface management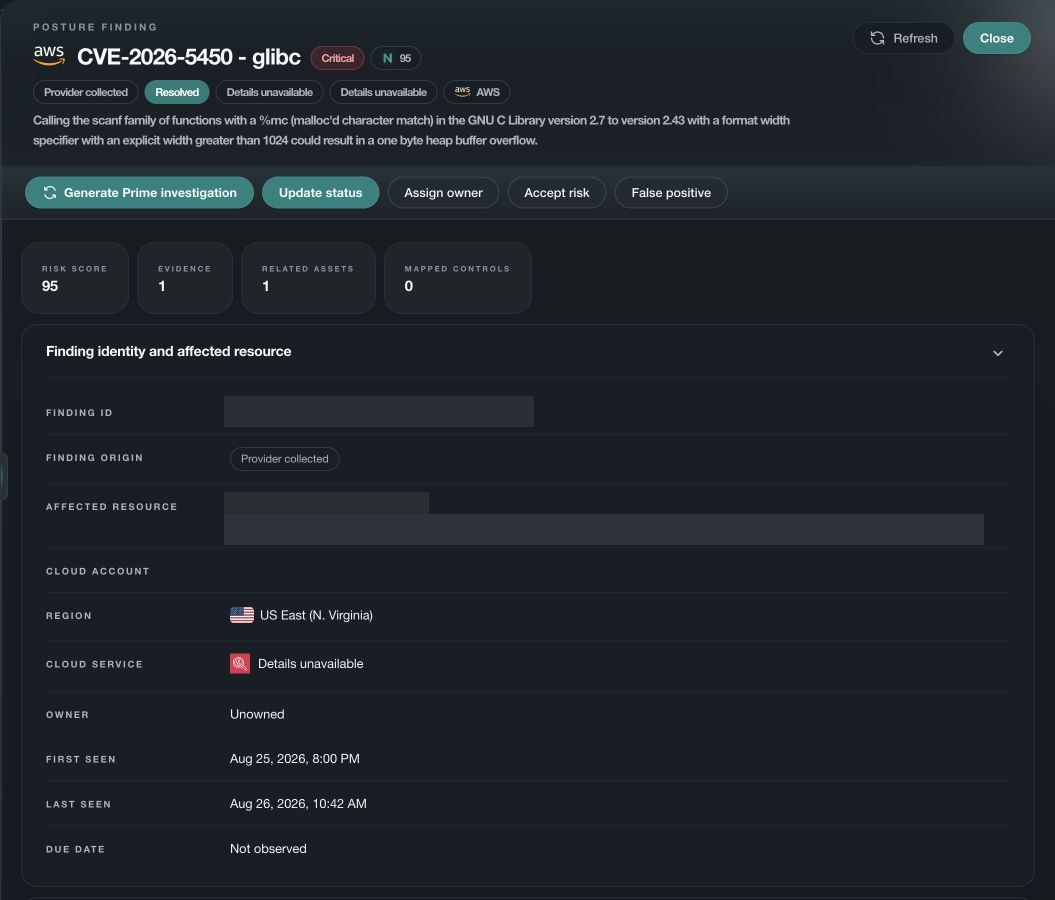
Reduce cloud risk
Prioritize the paths that can reach what matters.
Connected resource inventory
Review supported assets across cloud providers, accounts, regions and services.
Consistent asset identity
Keep resource names, provider identifiers, and asset details available for investigation and remediation.
Exposure and posture context
Relate public access, configuration evidence and security findings to the affected asset.
Ownership and lifecycle
Keep ownership, status, feedback and management history available with the resource.
FAQ
Questions about Cloud Asset Inventory.
What does Nova include in cloud asset inventory?
For supported sources, Nova presents the available resource identity, provider, account, region and service context. It can also connect exposure, posture findings, ownership and related evidence when those records are available.
How does Nova handle missing, stale or partial evidence?
Nova keeps complete, partial, degraded, unavailable, not applicable, not assessed and unknown states distinct. Missing evidence never becomes a passing control, normal behavior, low risk or proof that no threat exists.
Evaluate Nova
See how Nova fits your cloud security workflow.
In a private briefing, we will map Nova to your stack, confirm what connects and focus the evaluation on the outcome your team cares about.