
Detection operations
From alerts to analyst focus
Prioritize the work, not the noise.
Understand why an alert deserves attention before committing investigation time. NovaSignal brings the risk score and its explanation together with detection severity, Threat Intelligence, asset exposure, and available activity context. Analysts can compare changes over time and open the original alert or rule, keeping prioritization separate from the decision to confirm a threat or change a detection.
Incoming signals
Priority queue
Severity alone is not priority
A severe alert on an isolated test asset is different from the same behavior on an internet-exposed production identity. Nova brings that operational context into the priority queue.
From alert to investigation
- Observe
- Prioritize
- Investigate
See how work moves through Nova
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
Priority with context
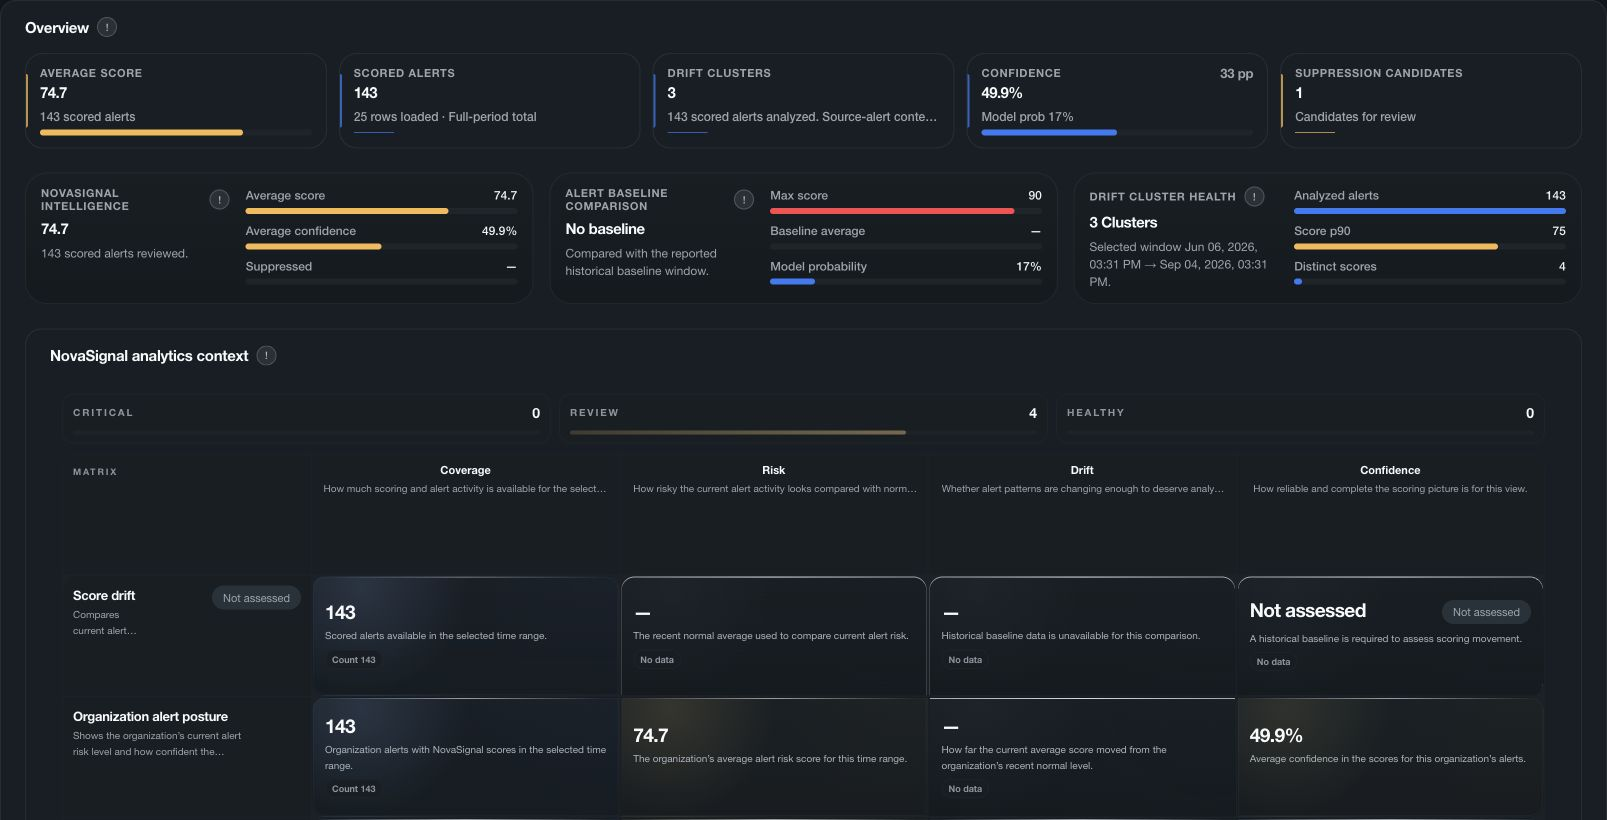
Give analysts more than a severity label.
Score, confidence, technique context, cloud scope, location and workflow actions appear in the same alert view, helping analysts decide where to begin.
Explore the analyst workflow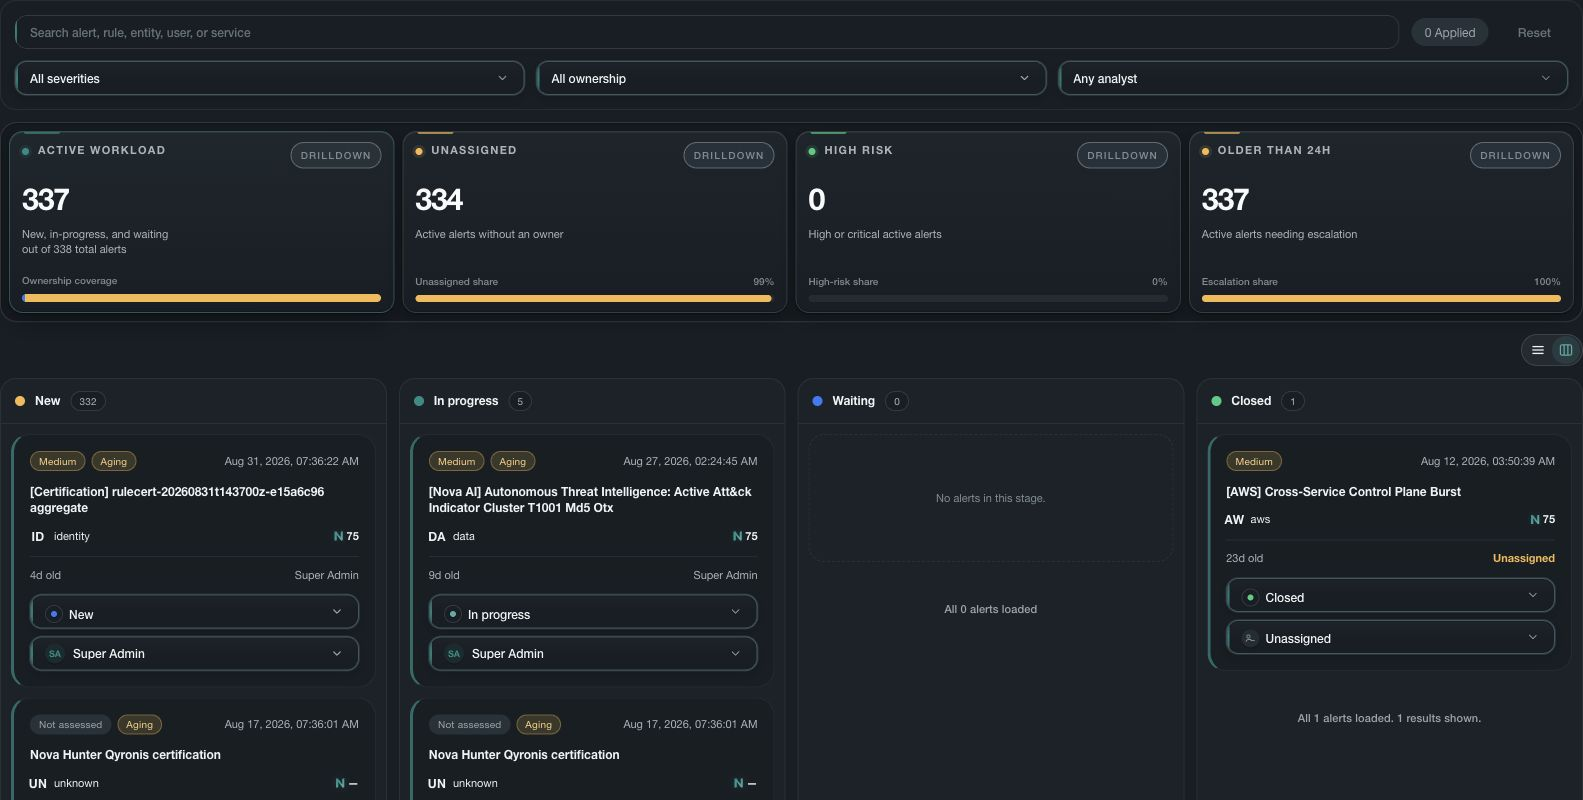
NovaSignal scoring
Separate the model signal from the final evidence-aware priority.
Review the factors behind NovaSignal's alert priority. A low machine-learning score does not cancel independently supported evidence of a serious threat.
Explore the NovaSignal scoring engine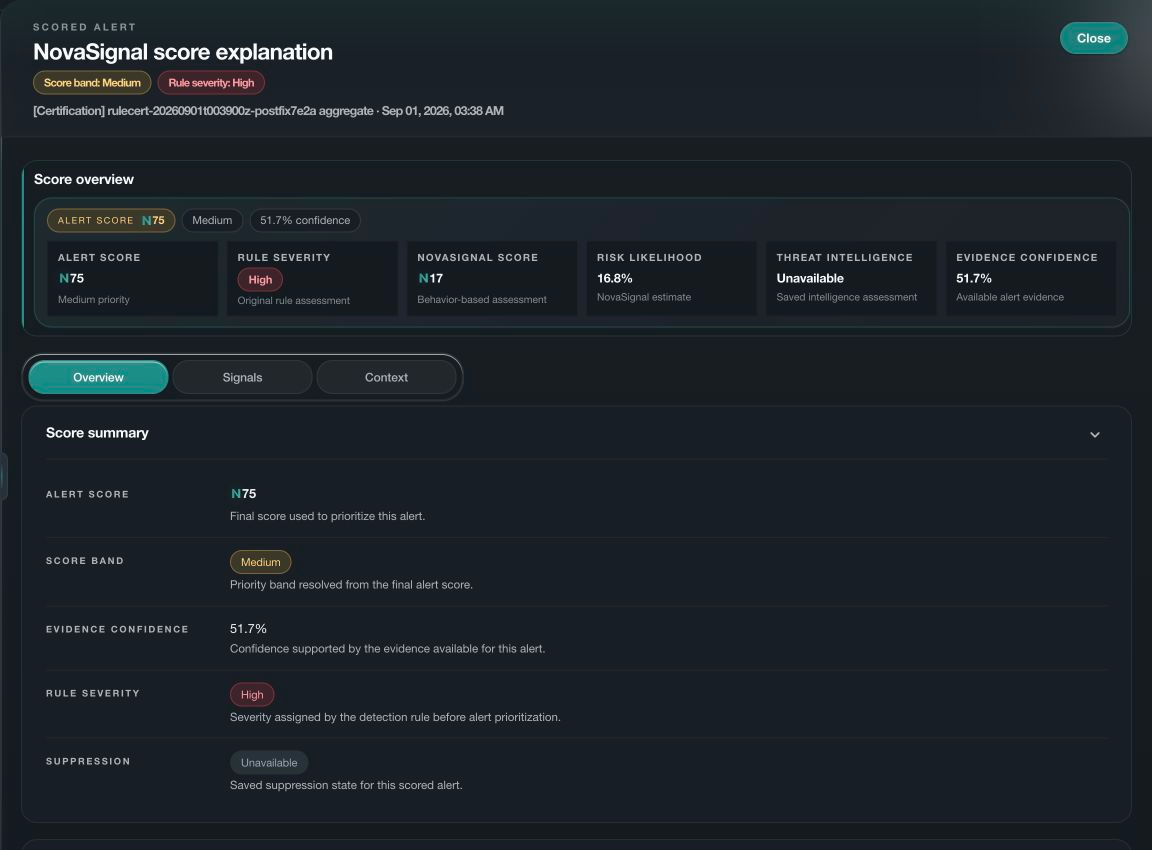
Detection health
Measure signal quality before the queue becomes the problem.
Coverage, confidence, alert rate, noise and score distribution give detection owners a reviewable view of where tuning attention is needed.
Explore detection engineering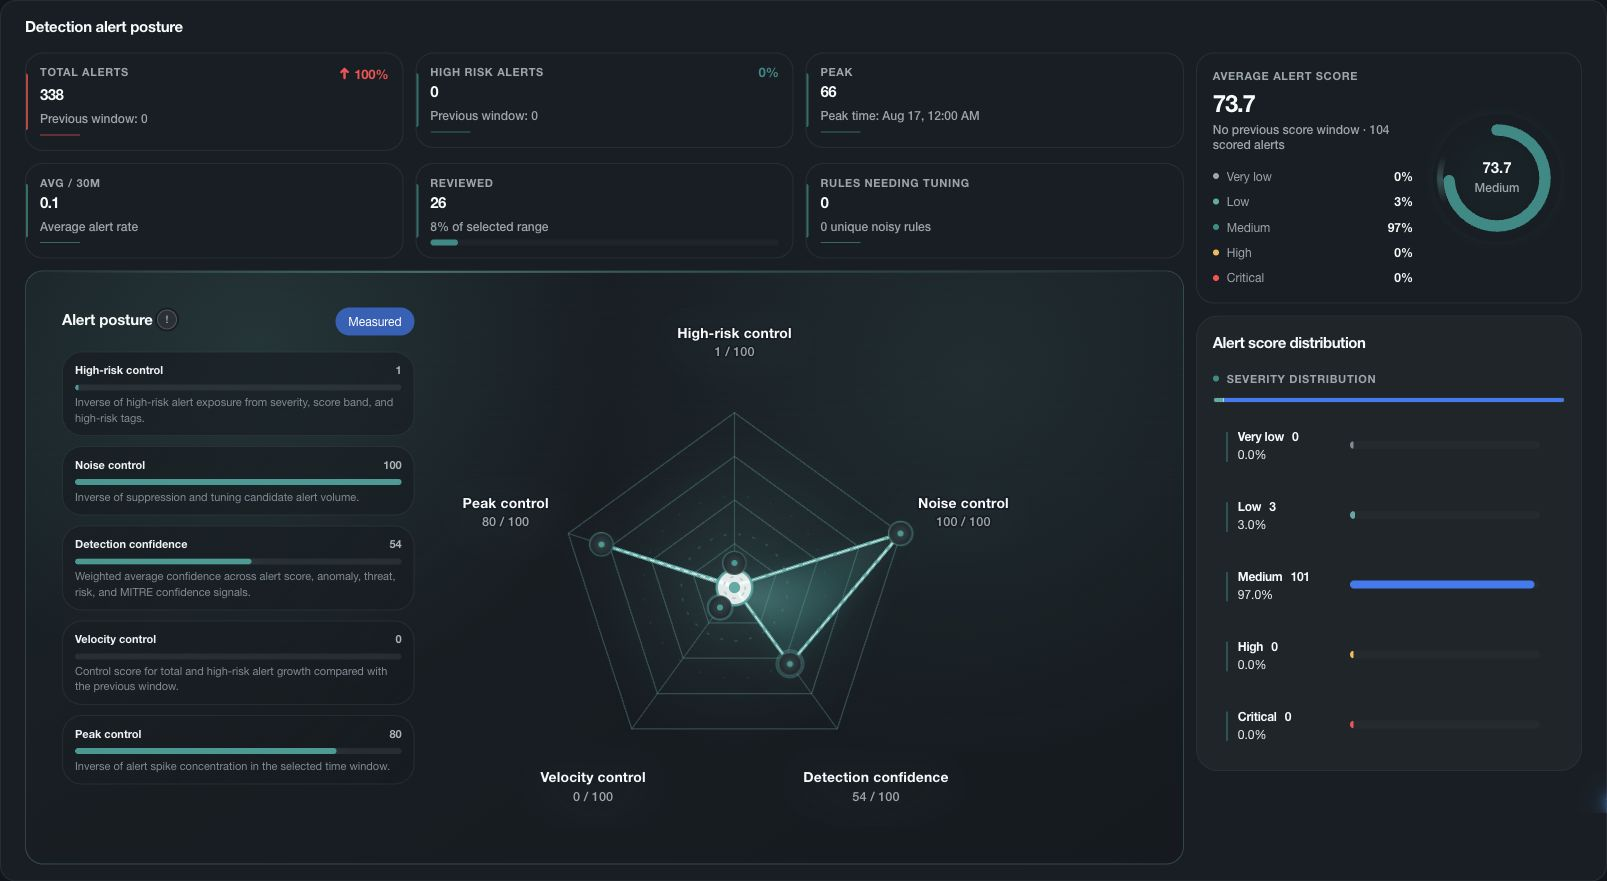
Strengthen security operations
Give analysts the context to act with confidence.
Explainable risk scores
Review alert, event, and exposure scores with their sources, confidence, and contributing factors.
Improve detection quality
Develop and validate detection logic while keeping quality, evidence and required review visible.
Cross-source context
Relate signals across security activity, identities, assets, findings and intelligence.
Explainable ranking
Use evidence and operational context to explain why one item is ahead of another.
Analyst feedback
Use analyst outcomes to improve future detection quality without changing the original evidence.
Evaluate Nova
See how Nova fits your cloud security workflow.
In a private briefing, we will map Nova to your stack, confirm what connects and focus the evaluation on the outcome your team cares about.