
Cloud security
Risk in operational context
Turn cloud weaknesses into prioritized risk.
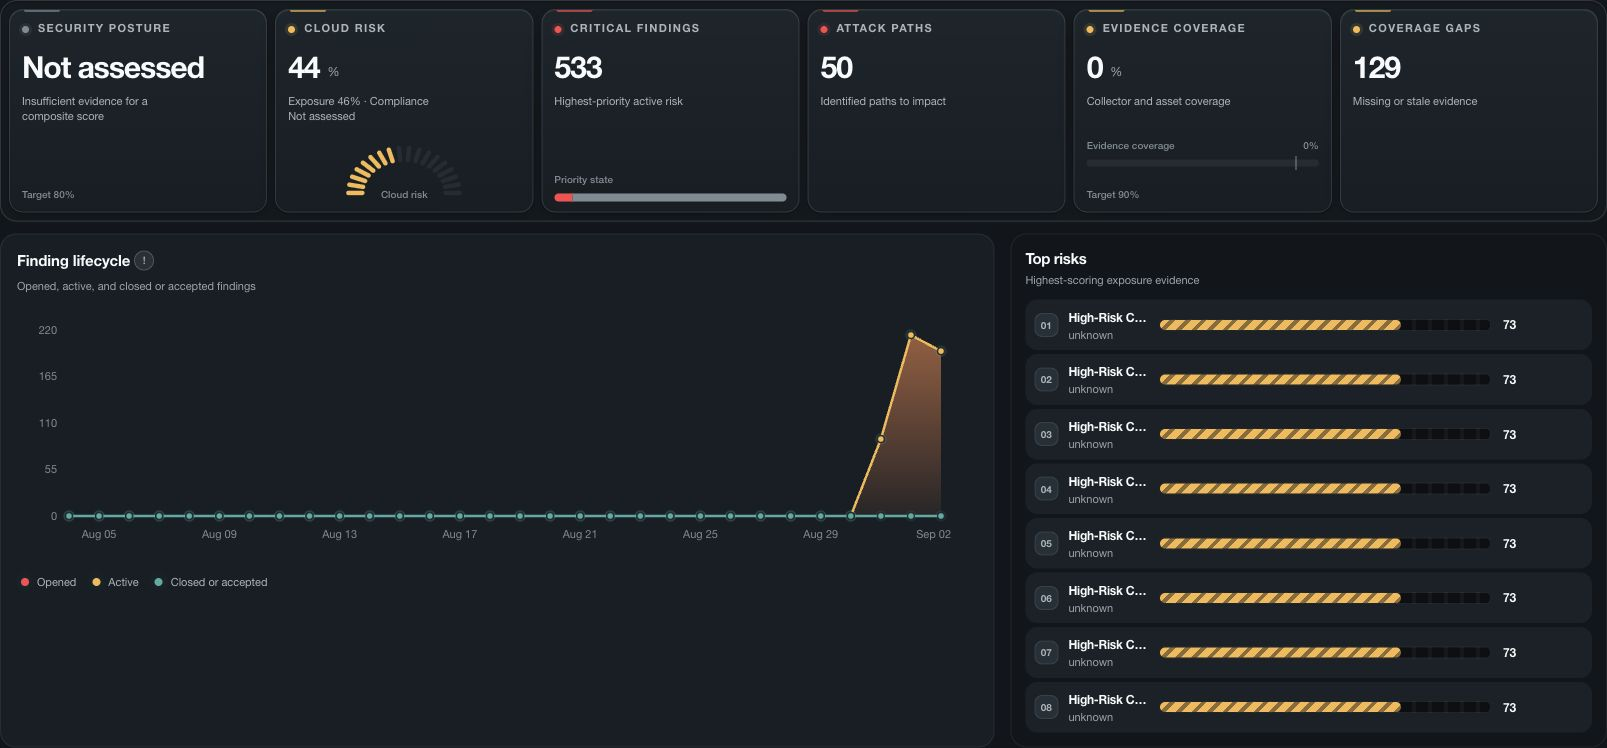
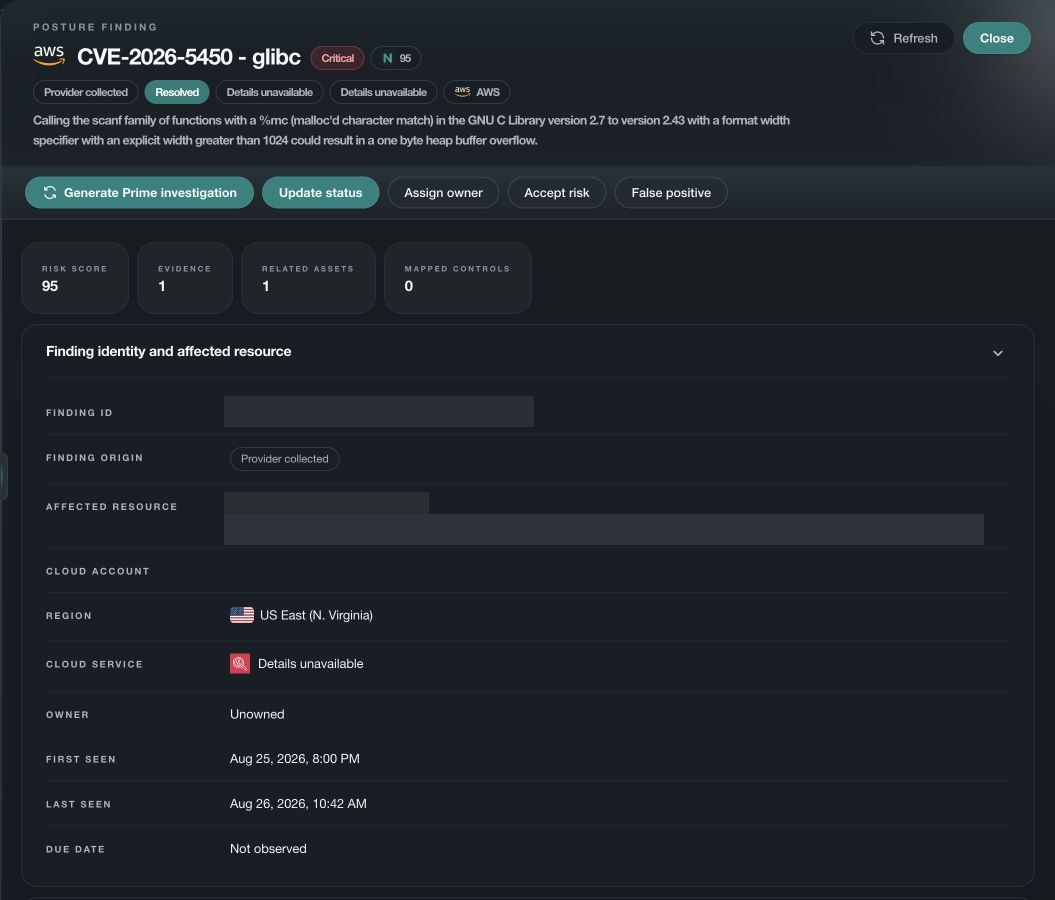
A configuration finding becomes more useful when the team can see what it exposes. Nova relates cloud weaknesses to affected assets, access relationships, public reachability, and potential attack paths. Review that context alongside threat activity and compliance evidence to prioritize remediation by the risk supported by your environment, rather than severity alone.
Cloud findings need exposure and threat context
See the affected asset, its exposure, related detections, and any safeguards before choosing a remediation priority.
Cloud risk path
- Inventory
- Exposure
- Priority
See how work moves through Nova
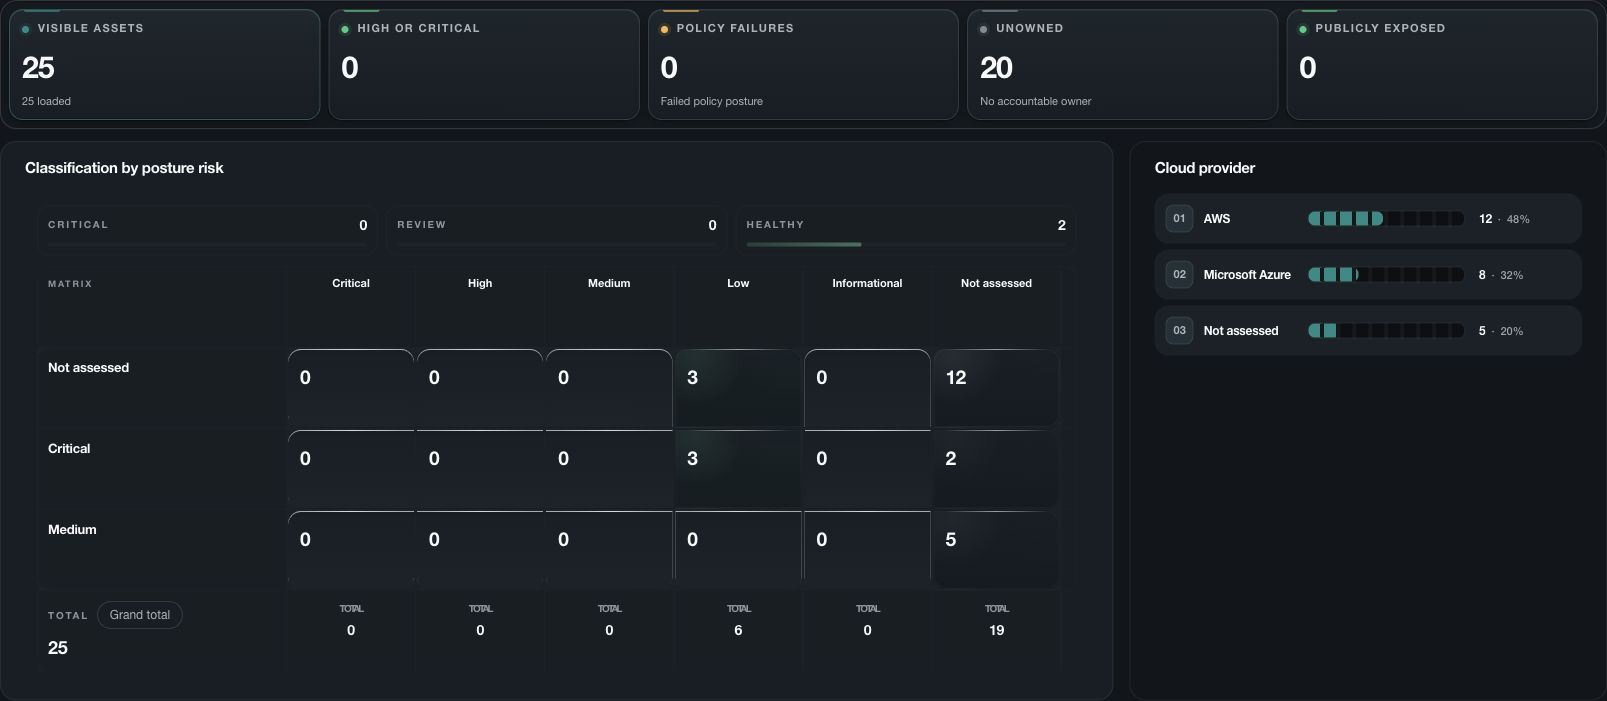
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
Strengthen security operations
Give analysts the context to act with confidence.
Multi-cloud configuration evidence
Assess supported AWS, Azure, Google Cloud and Kubernetes evidence through explicit controls.
Attack-path relationships
Connect identities, assets, exposure and findings to reveal the path, not only the issue.
Know where evidence is missing
Keep assessed, missing and incomplete evidence visibly different.
Remediation context
Route work with affected systems, evidence and ownership intact.
Evaluate Nova
See how Nova fits your cloud security workflow.
In a private briefing, we will map Nova to your stack, confirm what connects and focus the evaluation on the outcome your team cares about.