
Detection operations
Cloud detection and response with evidence
Detect suspicious activity. Connect it to exposure. Respond with control.
Investigate suspicious cloud activity with the affected identities, resources, access relationships, and related alerts in view. Use threat intelligence and behavior analysis to assess the incident, then prepare a supported response through DRX.
Observed sequence
Assessment
Cloud alerts often arrive without the context needed to act
Check what happened, which systems and accounts are affected, and whether internet exposure or access permissions increase the risk. Review any missing information before deciding to investigate further or respond.
From alert to investigation
- Observe
- Prioritize
- Investigate
See how work moves through Nova
Move through current product views one step at a time. Each view answers a different security question and keeps the available evidence and limits visible.
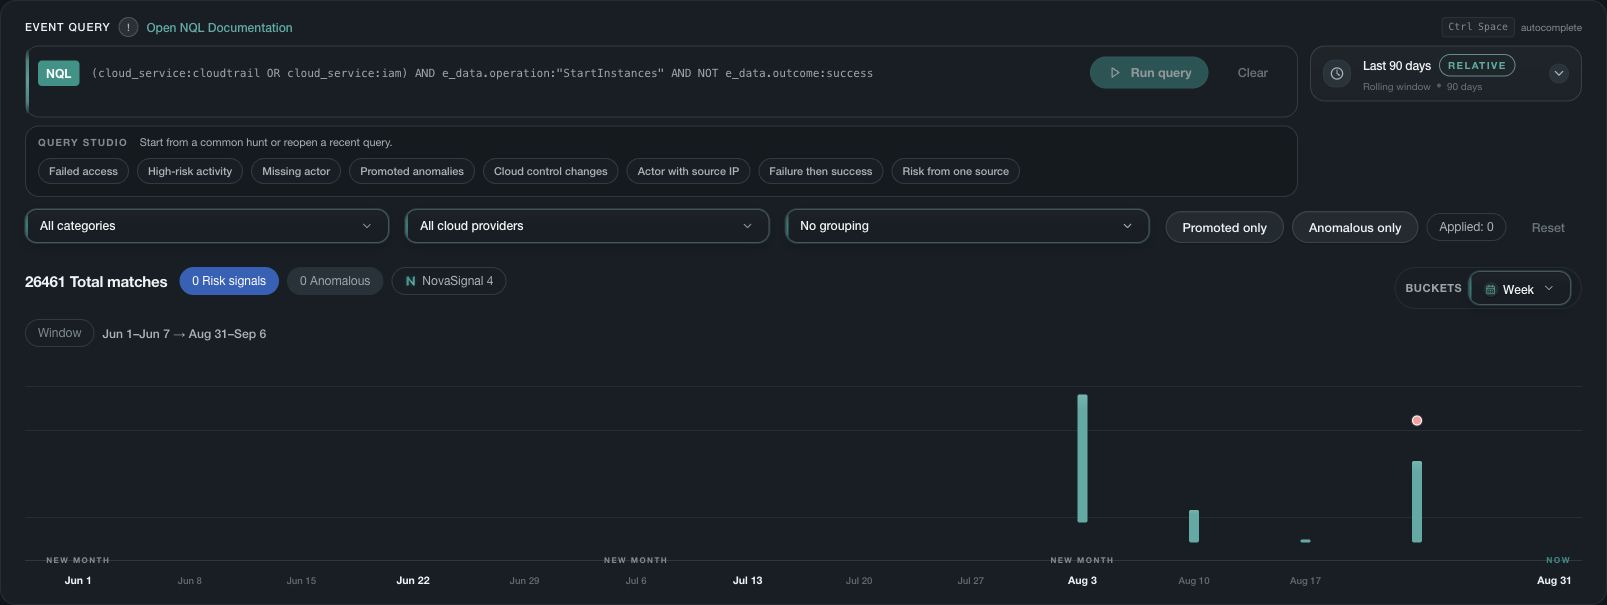
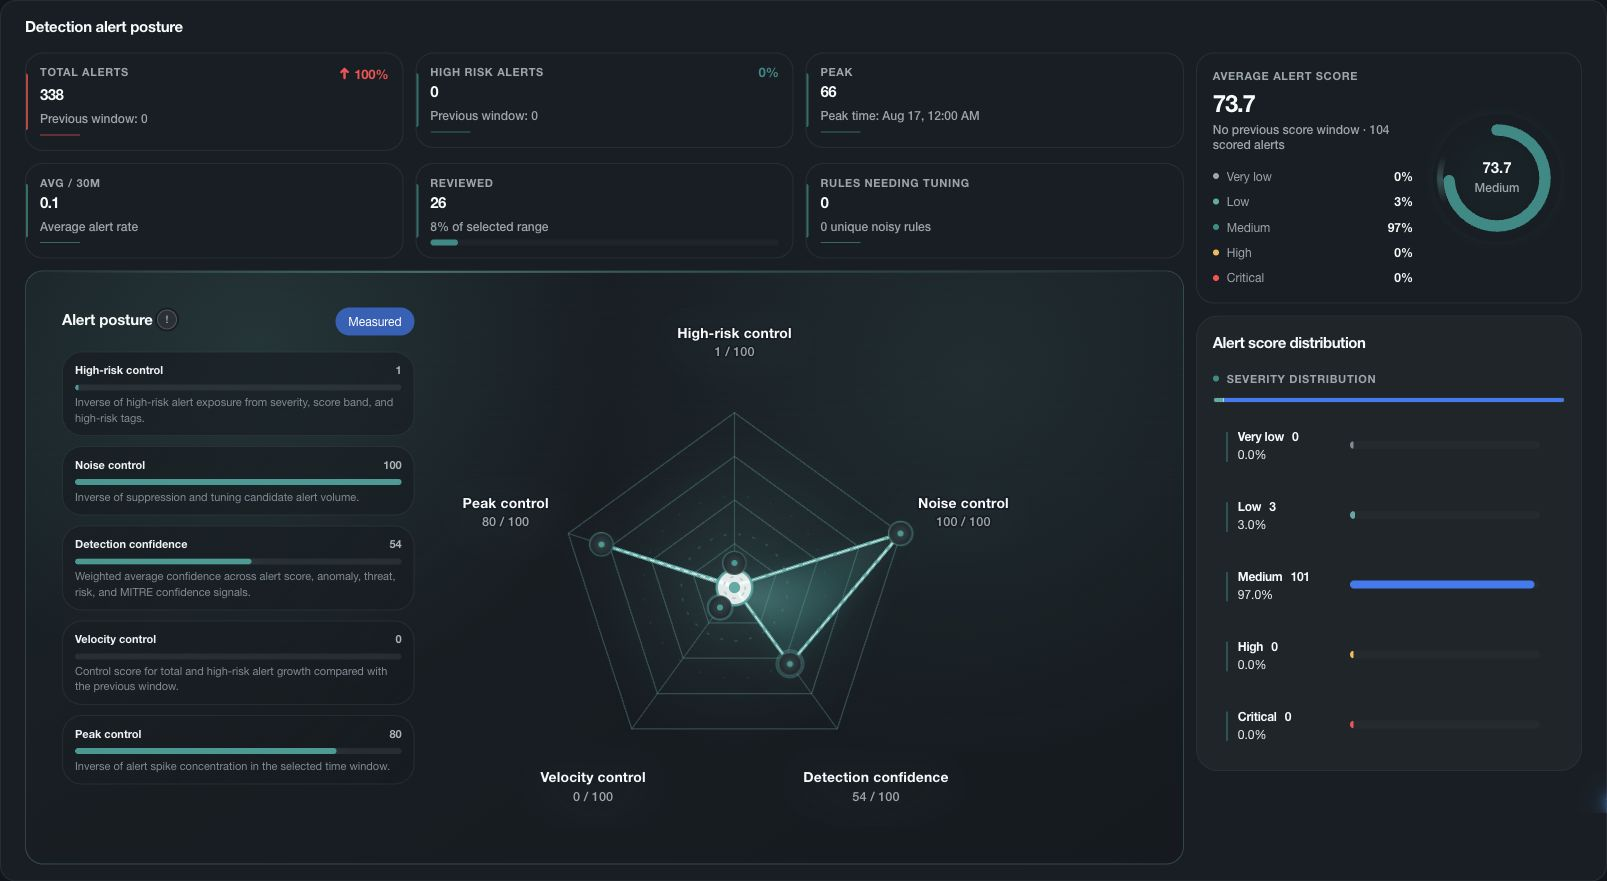
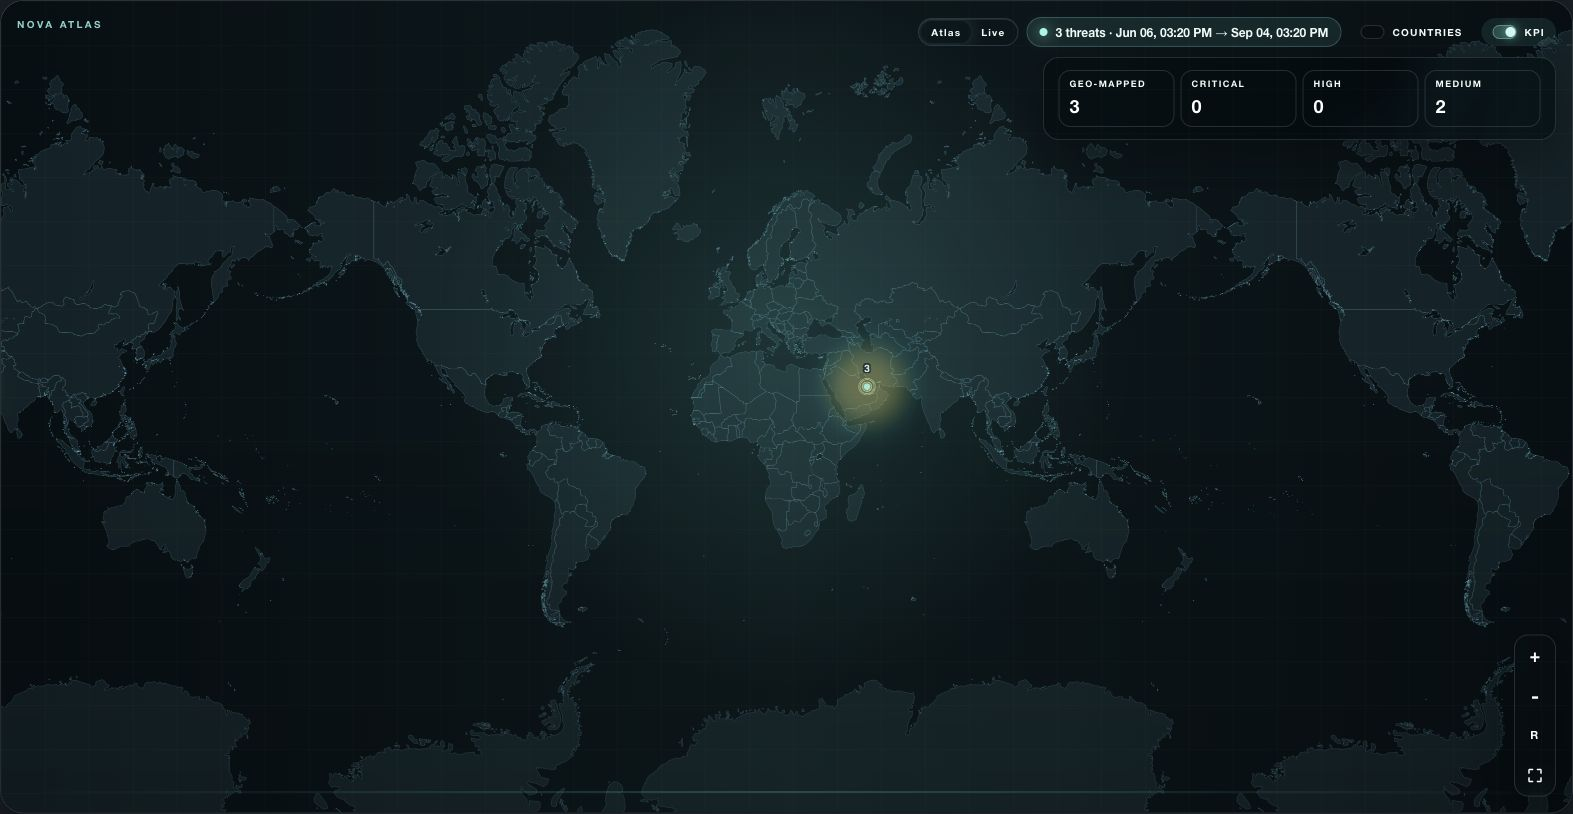
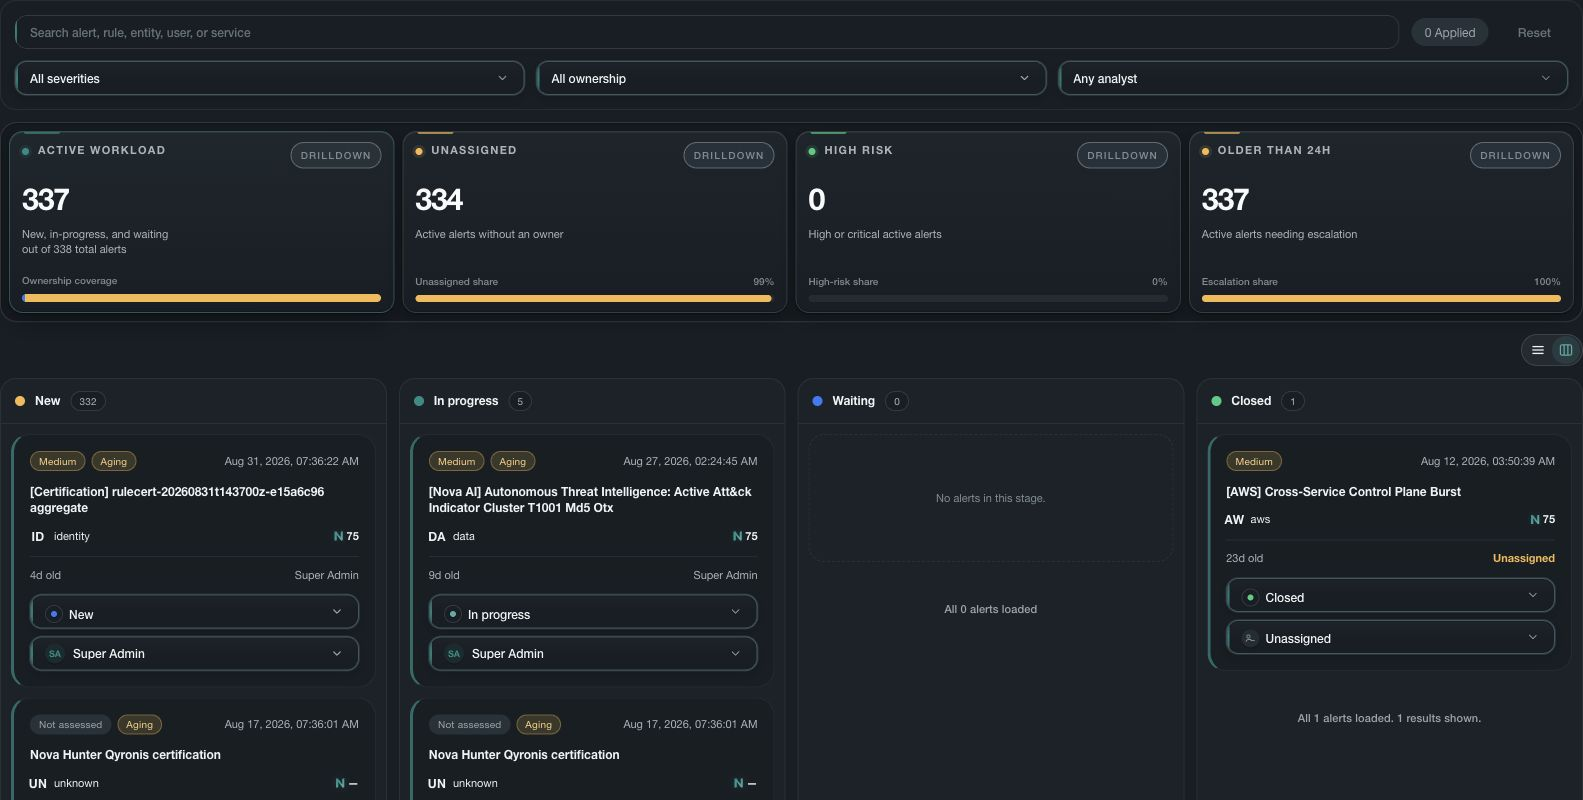
Reduce cloud risk
Prioritize the paths that can reach what matters.
Cross-source cloud threat detection
Correlate supported cloud, identity, container and SaaS activity to identify suspicious behavior.
Risk and exposure context
Prioritize activity with affected assets, identity relationships, attack paths, threat context and evidence quality.
Incident investigation
Keep search, chronology, related entities, original evidence and optional AI assistance in one case.
Policy-controlled response
Move verified decisions into approved actions when customer policy, connected-system support and required approval allow.
Blind spots stay visible
Show missing and incomplete evidence so silence never becomes a false all-clear.
Decision and response history
For supported, connected actions, preserve the decision, approval, progress and reported outcome.
FAQ
Questions about Cloud Threat Detection and Response.
What is cloud threat detection and response?
Cloud threat detection and response connects suspicious cloud activity to identities, assets, exposure and supporting evidence, then helps teams investigate and coordinate an authorized response. Nova keeps evidence quality, affected systems and progress visible through the supported workflow.
Does Nova automatically contain every threat?
No. A recommendation alone cannot run an action. The action must be supported by the connected system and allowed by the user's permissions and the organization's policies. Containment and other high-impact actions remain subject to the required approvals.
Which cloud environments and security systems can Nova connect?
Nova has evaluated connections across AWS, Microsoft Azure, Google Cloud, Kubernetes and supported identity, endpoint, software service, intelligence, ticketing and response systems. The available evidence and action set varies by connection and is confirmed for each customer environment.
Which response actions are available?
Action availability depends on the connected system, granted permissions, customer policy and enabled integration. Hansec confirms the supported action set, simulation behavior and approval requirements for each environment.
Evaluate Nova
See how Nova fits your cloud security workflow.
In a private briefing, we will map Nova to your stack, confirm what connects and focus the evaluation on the outcome your team cares about.