
Cloud security and security operations in one platform
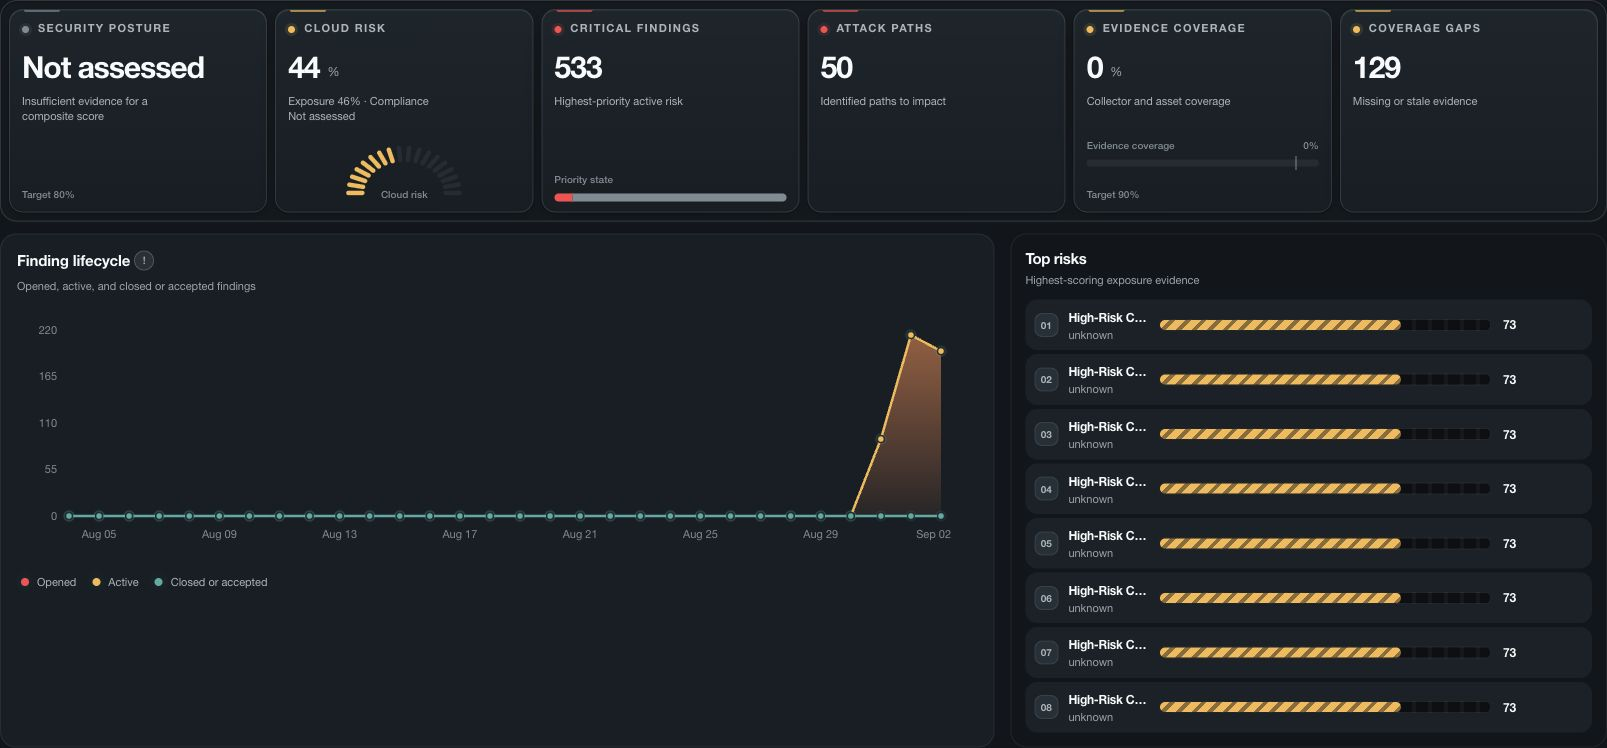
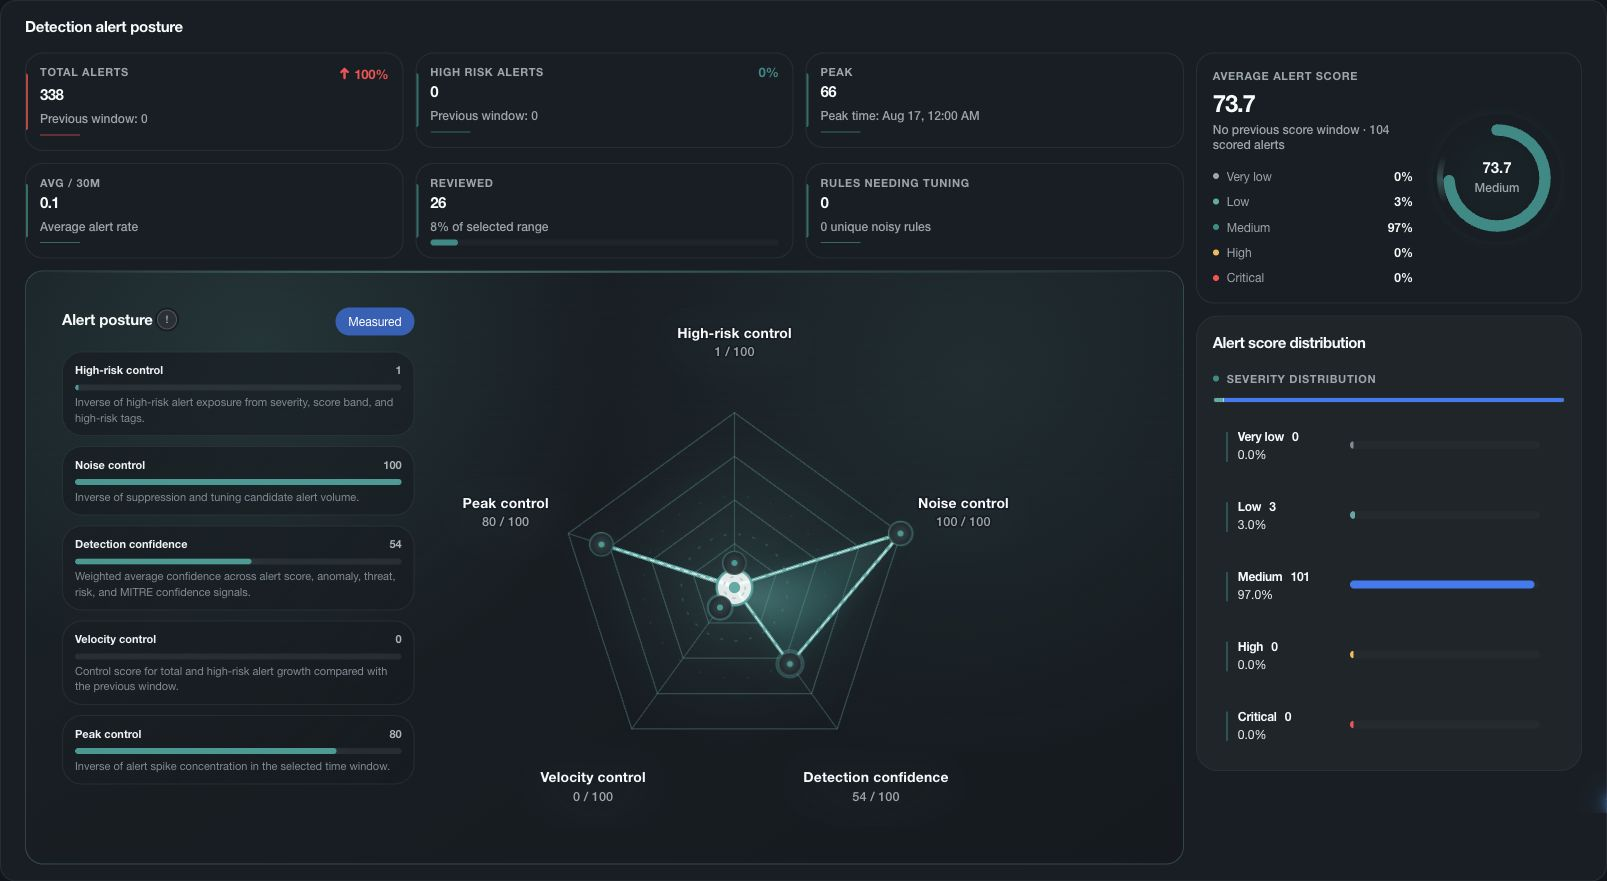
Nova brings cloud posture, exposure, behavior, threat context, detection, investigation, and supported response into a connected security experience. Teams can follow why something matters and which evidence supports the next decision without rebuilding the story between separate tools.
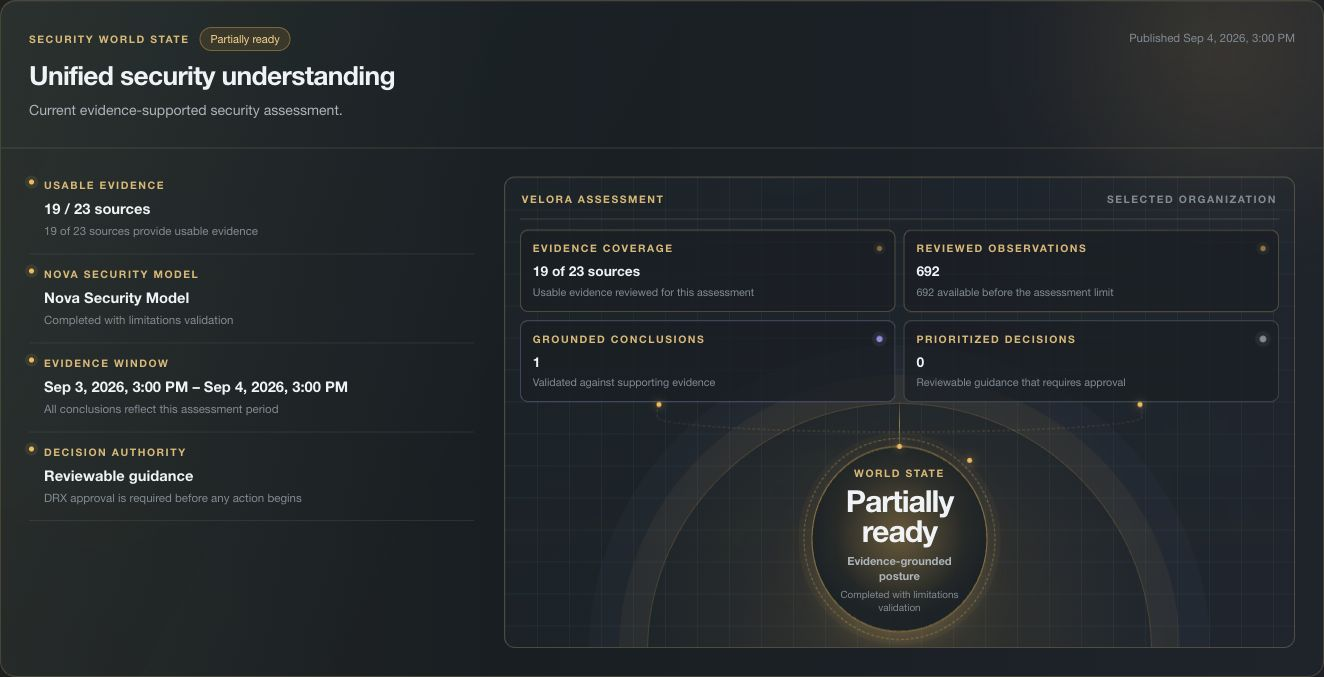
Nova preserves the difference between observed evidence, inferred conclusions, simulated possibilities, and missing assessment. A gap in evidence is never presented as proof that an environment is safe.
What teams use Nova for
- Understand cloud assets, posture, data exposure, attack surface, and reachable risk.
- Prioritize detections and findings with explainable evidence and confidence.
- Investigate related activity while keeping the assessment, unknowns, and ownership together.
- Measure detection and security coverage while keeping stale or incomplete sources visible.
- Prepare supported response actions using the customer's policies, permissions and approval requirements.
What Nova does not assume
A score does not replace the supporting evidence. A compliance view does not certify compliance. An AI-assisted conclusion does not grant permission to act. A supported connection does not mean every source produces the same evidence or action coverage.
Nova shows these limits so analysts can check the available evidence and decide whether further investigation is needed.