
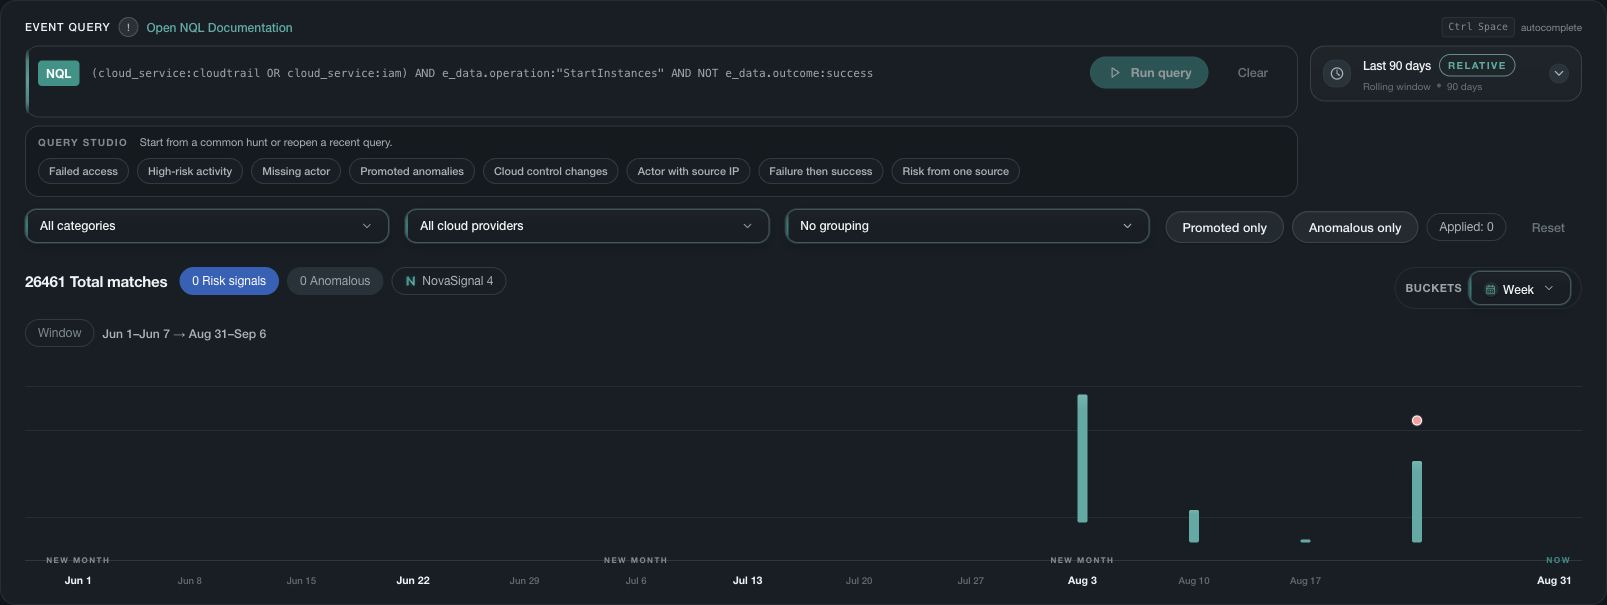
Start with a focused question
A useful event search states the question, customer scope, time window, expected sources, and known entities before adding conditions. Begin with the smallest safe query that can confirm the evidence is present, then narrow or expand deliberately.
Build an investigation path
-
01
Anchor
Choose a trusted event, alert, entity, or time that explains why the search begins.
-
02
Narrow
Apply time, source, field, and value conditions while watching result coverage.
-
03
Pivot
Follow related identities, addresses, assets, processes, resources, and techniques.
-
04
Compare
Check recurrence, baseline, related alerts, threat matches, and cloud context.
-
05
Preserve
Record the query meaning, time window, selected evidence, unknowns, and next step.
Interpret results carefully
No matches can mean the activity did not occur, the query is too narrow, the source is outside scope, evidence is delayed, fields differ, or the retained period does not include the event. Check source health, time zones, field meaning, and coverage before concluding absence.