
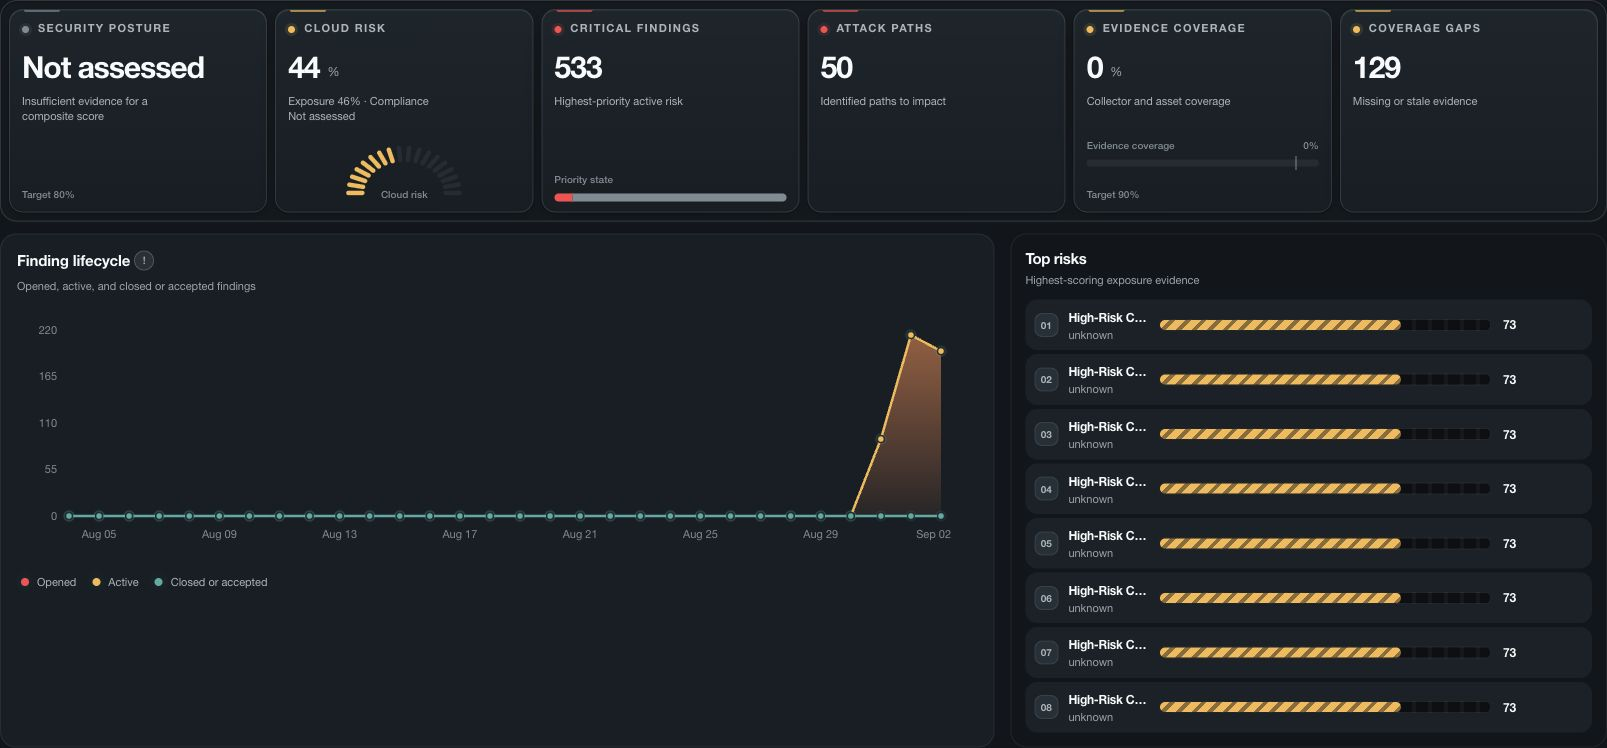
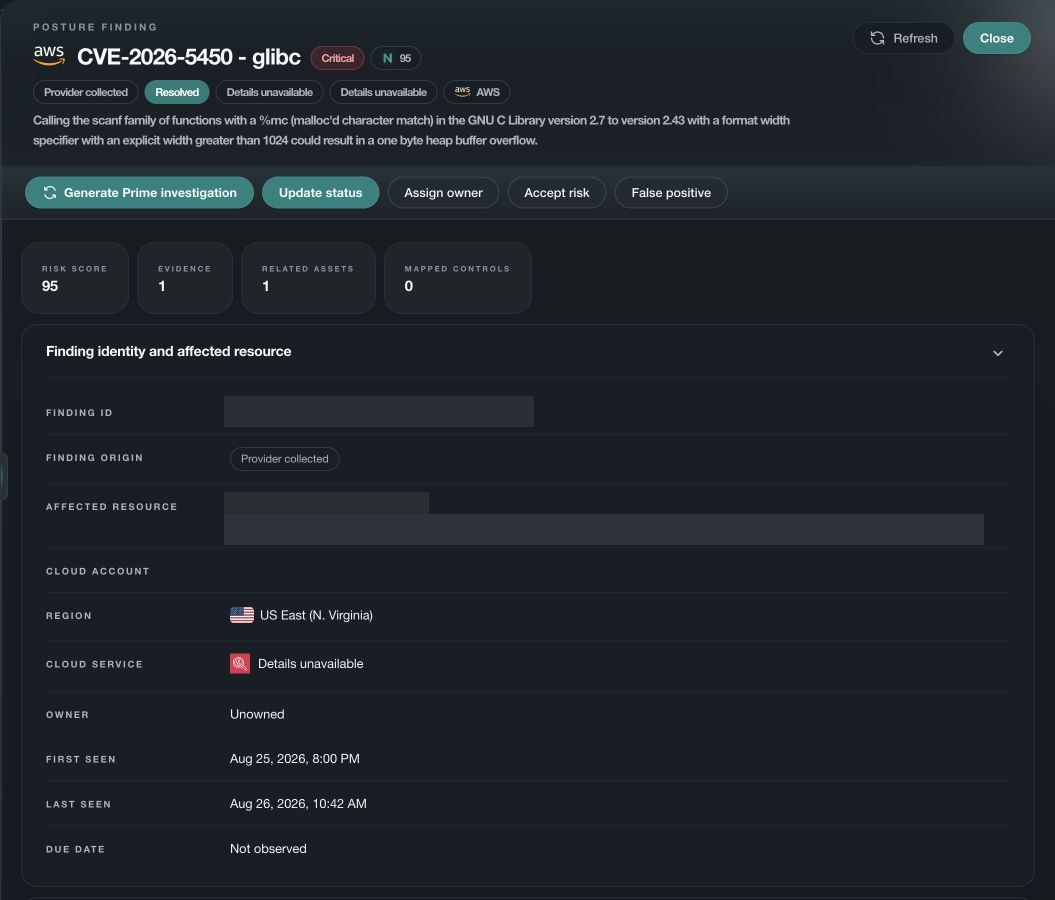
What an attack path represents
An attack path connects supported relationships that could allow progression from an entry condition to a more important system or outcome. It may combine exposure, configuration, network, identity, service, and data relationships.
A modeled path is a hypothesis for prioritization and validation. It does not prove that an attacker used the path. Observed events, alerts, or threat matches remain separate evidence and should be reviewed directly.
Review a path from both ends
- Confirm the entry point, the evidence supporting its exposure, and whether the condition is current.
- Inspect every relationship and note whether it is observed, configured, inferred, or unavailable.
- Review the destination asset, business importance, data context, and potential impact.
- Check for active evidence that raises urgency without treating its absence as proof of safety.
- Identify the smallest effective control change that can break or reduce the path.
Validate after a change
A path should be reviewed again after the provider change and after Nova receives current evidence for the affected relationships. Closing a task does not itself prove that the path no longer exists.