
What the attack surface shows
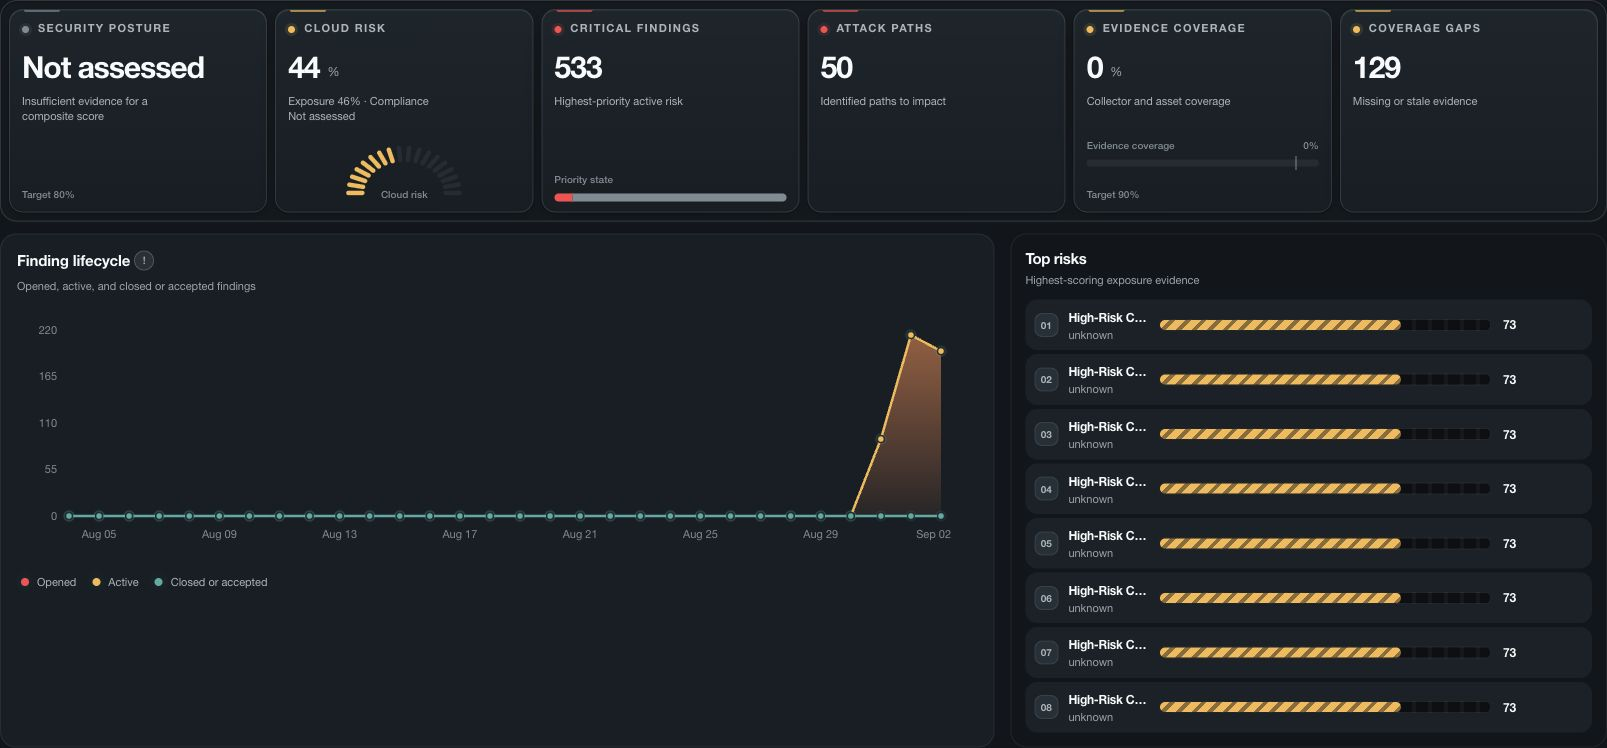
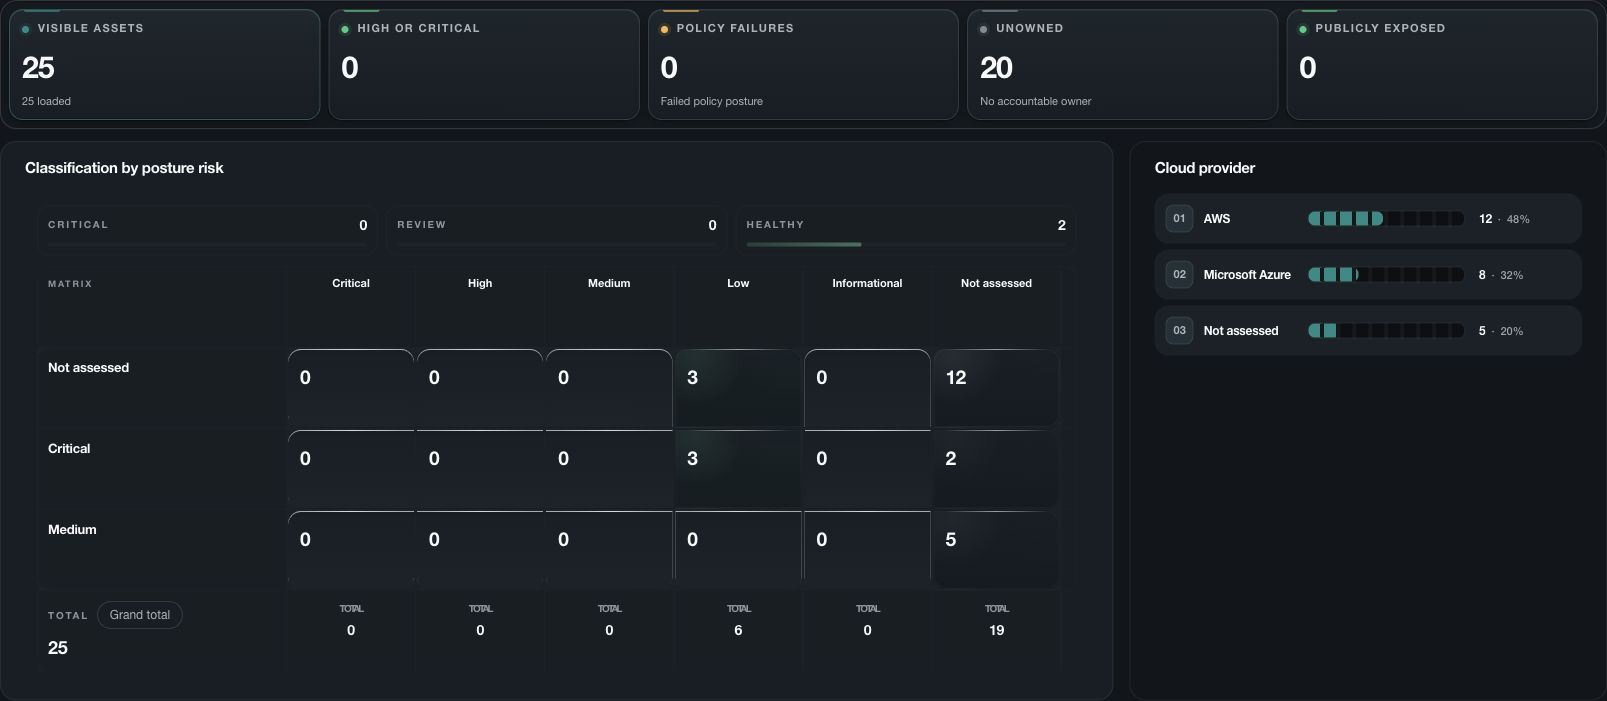
Attack surface management organizes supported evidence about externally reachable assets and services. It helps teams identify what appears exposed, which cloud or business context is connected, whether an owner is known, and which security conditions deserve validation.
Triage external exposure
- Confirm the observed address, service, certificate, hostname, cloud resource, and evidence time.
- Determine whether the exposure is expected, approved, documented, and assigned to an owner.
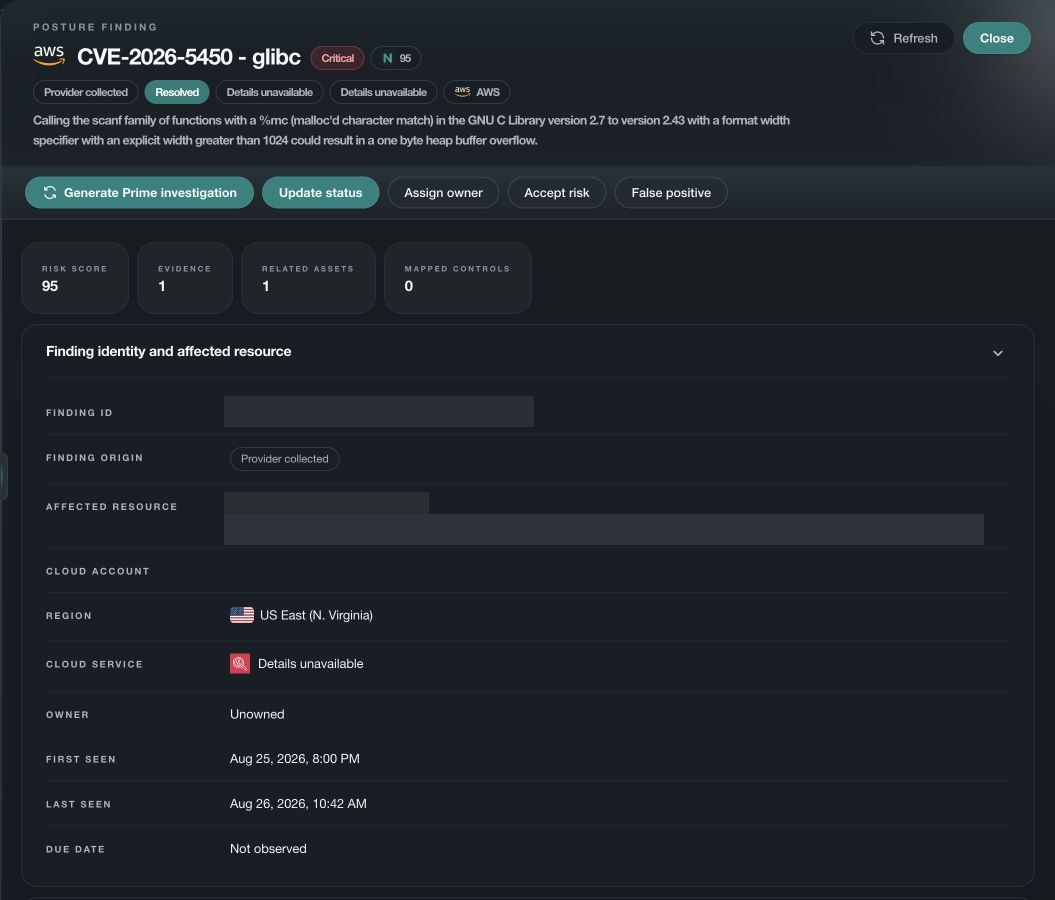
- Review posture findings, reachable relationships, sensitive data, privileged identities, and active threat context.
- Check whether the service is temporary, stale, duplicated, or outside the intended customer scope.
- Record the validation result and the approved change or exception path.
Avoid false certainty
External discovery depends on the observed scope, provider evidence, timing, and supported methods. An absent asset is not proof that no exposure exists. An observed endpoint is not automatically malicious or unauthorized. Validate both the technical evidence and business ownership.