
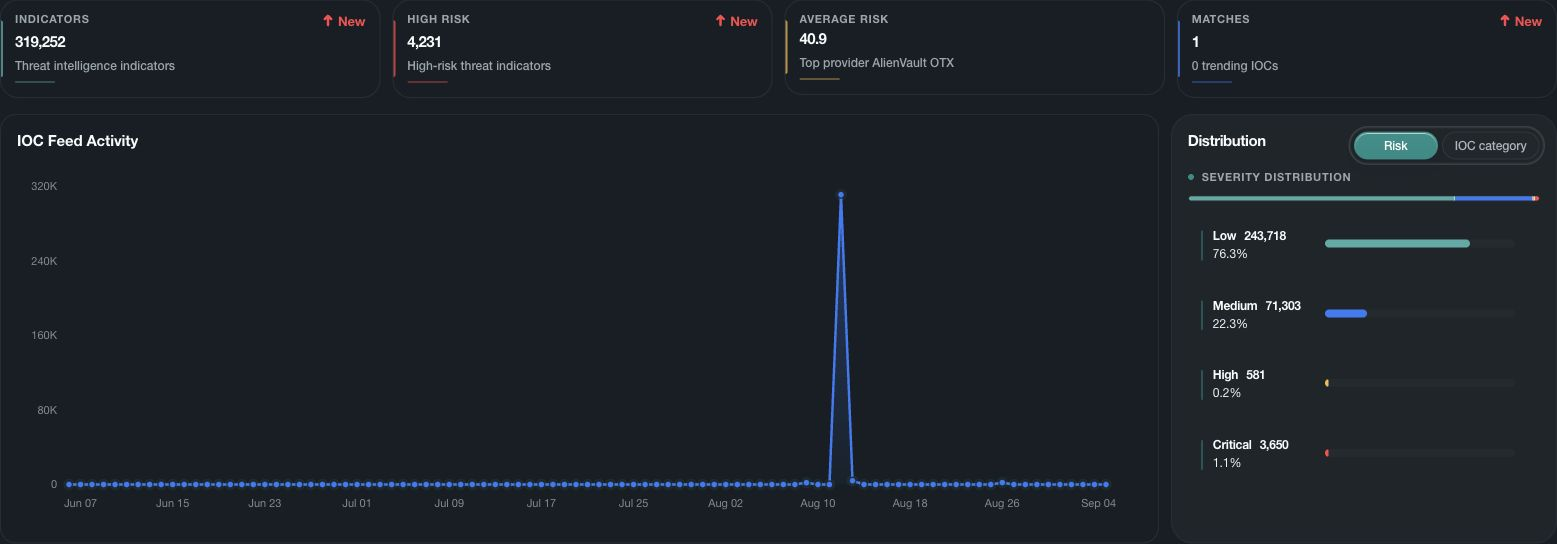
Intelligence adds context
Threat intelligence can describe indicators, vulnerabilities, malware, campaigns, techniques, actors, infrastructure, and reported activity from supported sources. Nova uses that context to help analysts ask whether a known concern is relevant to the customer environment.
Source quality, observation time, confidence, indicator lifetime, and independent evidence matter. A widely reported indicator is not automatically active or relevant in every environment.
Validate a threat intelligence match
- Confirm the exact indicator, type, source, confidence, first and last observation, and current status.
- Review the matching customer event in full source, time, direction, and entity context.
- Check whether shared infrastructure, address reuse, translation, proxying, or benign services could explain the match.
- Look for related behavior, recurrence, affected assets, cloud exposure, and other independent evidence.
- Record the supported assessment and unknowns before escalating or blocking activity.
Read relevance and coverage together
Threat Relevance helps focus on intelligence connected to the environment’s observed evidence and exposure. A relevant item still requires validation. A missing match can reflect no observed activity, missing sources, retention limits, unsupported fields, or incomplete assessment.