
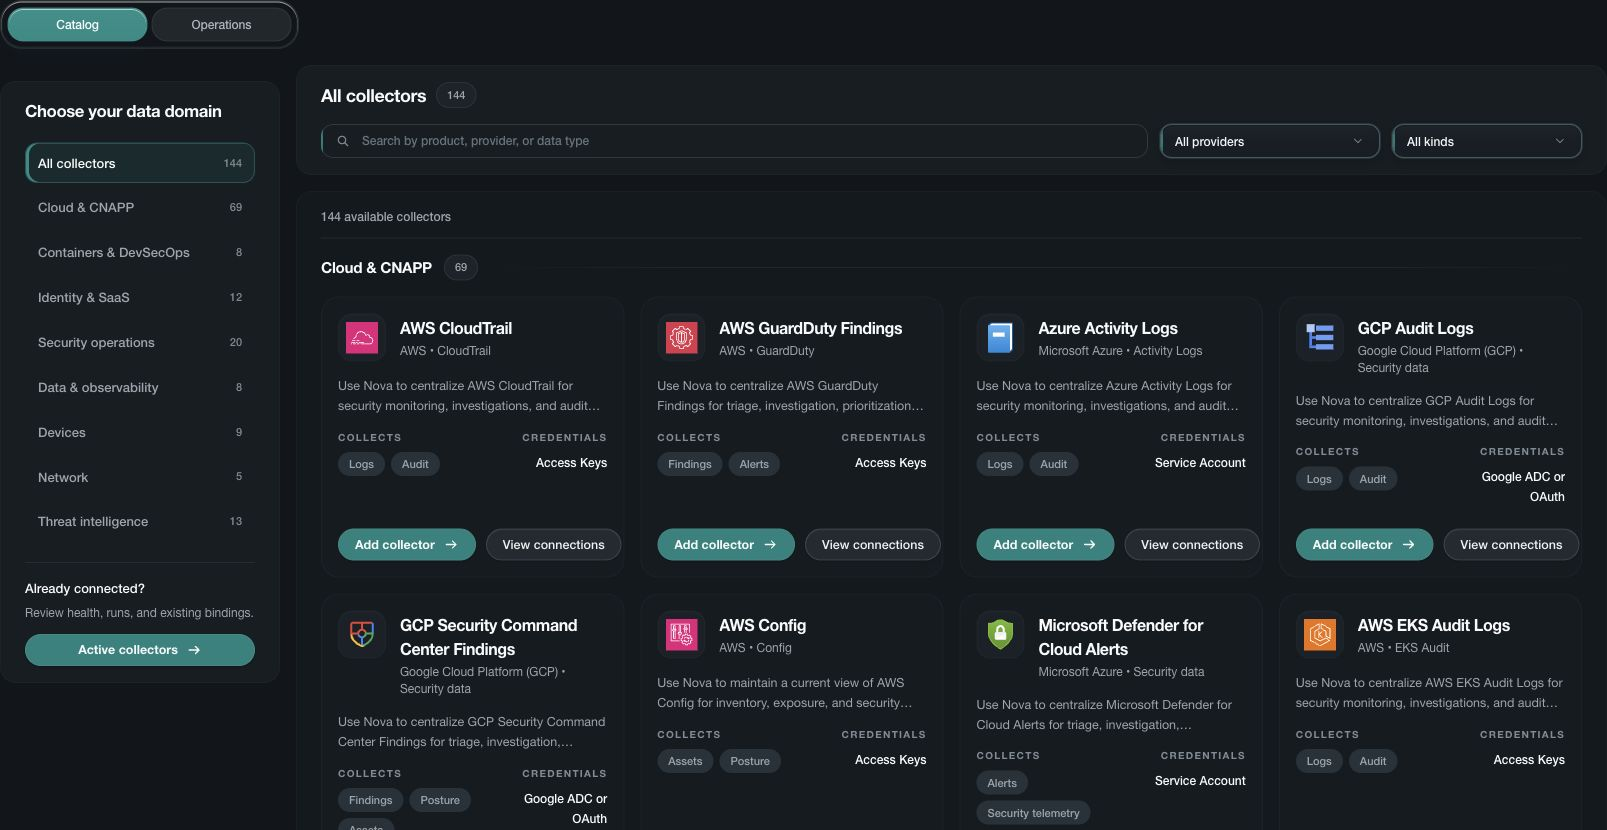
What a collector adds to Nova
A collector brings a defined family of customer-authorized security evidence into Nova. Depending on the source, that evidence may include activity records, cloud or device assets, security findings, relationships, or threat intelligence.
The catalog below reflects implemented Nova collectors. It is an evaluation guide, not a promise that every source is included in every subscription or available in every region and product plan.
Browse supported collector families
- Supported AWS collectors
- 30 implemented collectors covering the sources and use cases described in this guide.
- Supported Microsoft and Azure collectors
- 29 implemented collectors covering the sources and use cases described in this guide.
- Supported Google Cloud and Workspace collectors
- 17 implemented collectors covering the sources and use cases described in this guide.
- Supported Oracle Cloud collectors
- 3 implemented collectors covering the sources and use cases described in this guide.
- Supported identity and access collectors
- 6 implemented collectors covering the sources and use cases described in this guide.
- Supported endpoint and device collectors
- 9 implemented collectors covering the sources and use cases described in this guide.
- Supported network and email security collectors
- 10 implemented collectors covering the sources and use cases described in this guide.
- Supported vulnerability and posture collectors
- 10 implemented collectors covering the sources and use cases described in this guide.
- Supported data, SIEM, and streaming collectors
- 6 implemented collectors covering the sources and use cases described in this guide.
- Supported container and DevOps collectors
- 8 implemented collectors covering the sources and use cases described in this guide.
- Supported SaaS audit collectors
- 3 implemented collectors covering the sources and use cases described in this guide.
- Supported threat intelligence collectors
- 17 implemented collectors covering the sources and use cases described in this guide.
Choose sources by the outcome you need
- For security operations, prioritize activity, alert, identity, endpoint, network, and threat-intelligence sources.
- For cloud security, prioritize inventory, posture, finding, identity-relationship, exposure, and flow sources.
- For vulnerability programs, combine asset and finding sources with ownership, exposure, and exploit context.
- For detection and hunting evaluations, choose sources that represent the activity, entities, and threat questions your team needs to test.
Confirm fit before onboarding
-
01
Define the question
State the investigation, posture, coverage, or reporting outcome the evaluation must prove.
-
02
Select the evidence
Choose only the collectors that can supply the required records, assets, findings, or intelligence.
-
03
Confirm source coverage
Check the product plan, available history, regions, accounts, and source-side scope with Hansec.
-
04
Measure freshness
Agree how collection health, delay, gaps, and expected volume will be judged during the evaluation.